GitHub is updating its policy and will start using your code and data to train AI using Copilot.
From April 24, your Copilot chats will be used by default to train their AI models. This includes your prompts, the code it suggests, and related context.
Deactivate it ASAP.
This is an old writeup by @ozgur_bbh from four years back, a very successful #bugbounty hunter.
I feel it still holds relevance if you're planning to start doing it as a side gig, even in 2025. Link 👇
Apply to attend #PHTalks in Jakarta, Indonesia 🇮🇩
🗓 July 23 — free in-person event
🔗 https://t.co/35piUWzBRV
CFP open until July 4.
Attendee registration open until July 11.
I’m reaching out to offensive and defensive security people — red/blue teams, SOC, DFIR, vuln, and bug bounty researchers across Indonesia and the region.
Know people? Let me know.
Hello everyone ♥
a little bit write-up of #bugbountytip#bugbountytips I am going to write here .....
Title:
getting unauthorized access on 3rd party's/workspaces & and building your checklist for quickly locating bugs there via massive recon
we know that its helpful to look for google
groups/docs/etc..
Slack as well just like when the amazing @h4x0r_dz shared days ago ..
Use google dork "site:https://t.co/ravW2tHHcP"
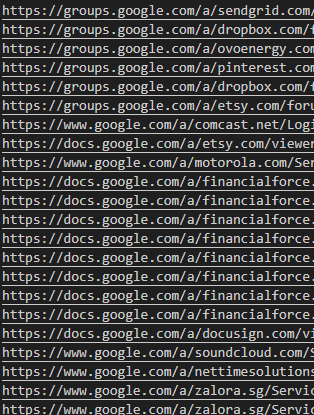
so I was not in a good mode the last months to doing Google Dorks, so what I did was build a checklist ready for me & very huge one
for EX:
https://t.co/wPxAHXvC18
https://t.co/hs3VHvhT92
https://t.co/ravW2tHHcP
and here is just an example you can add more similar workspaces for your checklist
thin I extracted all internet endpoints and as example here join[.]slack[.]com
https://t.co/OlHQSEQ6Qz
https://t.co/e8jB8H6nMS
https://t.co/w5h4VkESyQ
you can use the ready tools to do it such as waymore
important note: you have to keep your checklist updated every week
and from here I just keep looking for the company name or domain name to see if there's anything connected
and mostly the company name or domain name in the URL it self EX: tesla
https://t.co/QesyI4MHu2
Ex For Bugs found:
1 unauthorized access to the workspaces
(PII | Information disclose)
2 account takeover as Ex: valid signup employee link
3 account takeover as Ex: valid reset password employee link
now about Slack, as an example if you found an invitation link for tesla
Tesla https://t.co/QesyI4MHu2 and that link was not valid, don't stop here
it will redirect for Ex:
tesla-internal[.]slack[.]com
here back and start looking manually for endpoints of this subdomain as well EX:
https://t.co/w2dhvfdBhL
now there are a lot of 3rd party's/workspaces I just shared here
slack & Google Docs/groups
What I wrote is a bit long and annoying to some, so I apologize. I hope, as usual, that this will be useful to all who follow me here.
#Bugounty
don't forget to retweet if you like it ♥♥♥
All my current bug bounty knowledge is gone.
Here's how I get it back and make $100k in the first year:
First, I've got to learn the basics. For this, I will make sure I understand at a high level how the components I'm working with function.
I'll need to understand...