Since the @NCSC has been quiet on the MiCODUS MV720 GPS trackers, I thought I'd take matters in my own hands and report on this timely issue, both here and abroad. Shoutout to @kripthor for the brilliant research and to @BitSight@CISAgov@ICSCERT for the joint disclosure🤝
@BitSight has discovered six severe #vulnerabilities in a popular GPS tracker potentially allowing #hackers to track individuals, remotely disable fleets of corporate supply and emergency vehicles, abruptly stop civilian vehicles, and more. Learn more 👉🏼 https://t.co/3PI8K1qnLS
I’ve been a security engineer for a whole ass year now. Here are a few Infosec training resources shared w/ me that have been helpful over the last year in my role:
🧵1/10
We've all received emails with no attachment and assume it's "safe" to open in a mail client (as long as we don't explicitly click on any URLs). Right?
Not so much...
DemonSeed EDU is here
Learn hardware hacking by making your own malicious USB cables. Every kit is a 2 pack. Share one with a friend? 🌚🔥
#OMGDemonSeedEDU
https://t.co/N3skAGdjZh
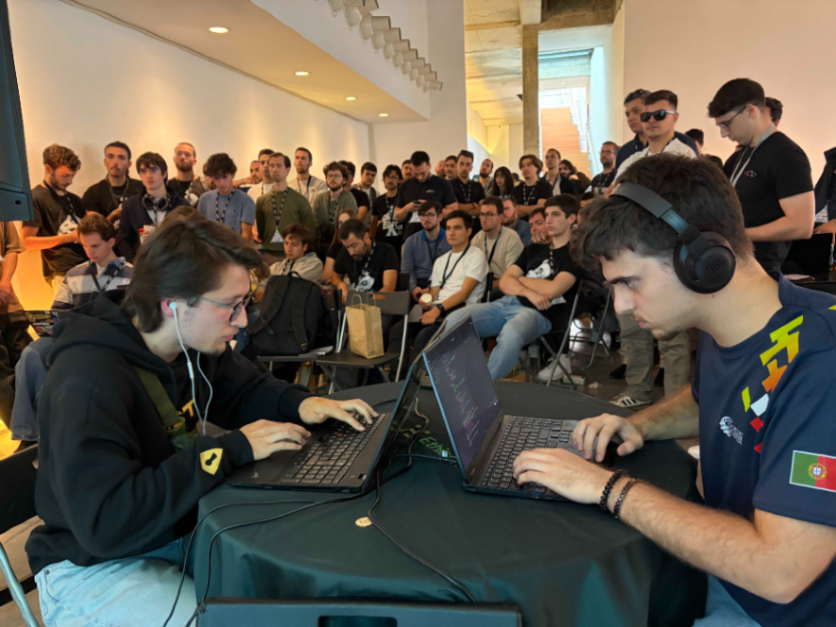
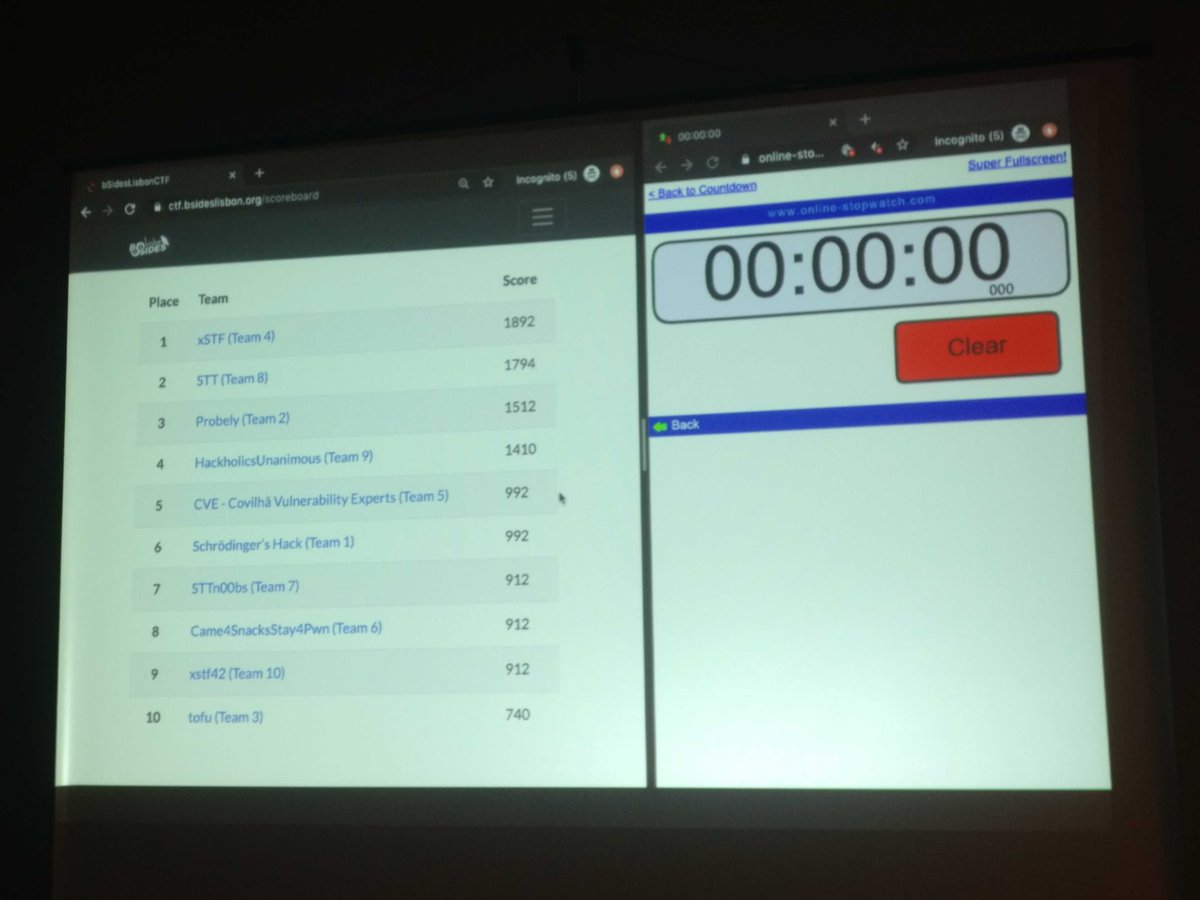
We are the winners of @Bsideslisbon CTF for the second year in a row! Thank you @Bsideslisbon for another amazing CTF and conference. See you all next year 🍻
Attention all teams qualified for the CTF finals tomorrow: Check your email! Make sure you're there on time, and remember to bring a WiFi card that supports monitor mode, and scotch tape... :)
CTFs encourage you to think creatively about bugs you know exist, bug bounties require knowing where bugs might be. @0xACB talked about how his #CTF experience translates to #bugbounty and how he went from 0 bugs to MVH in 1 month! https://t.co/gwleSwrE8B #TogetherWeHitHarder