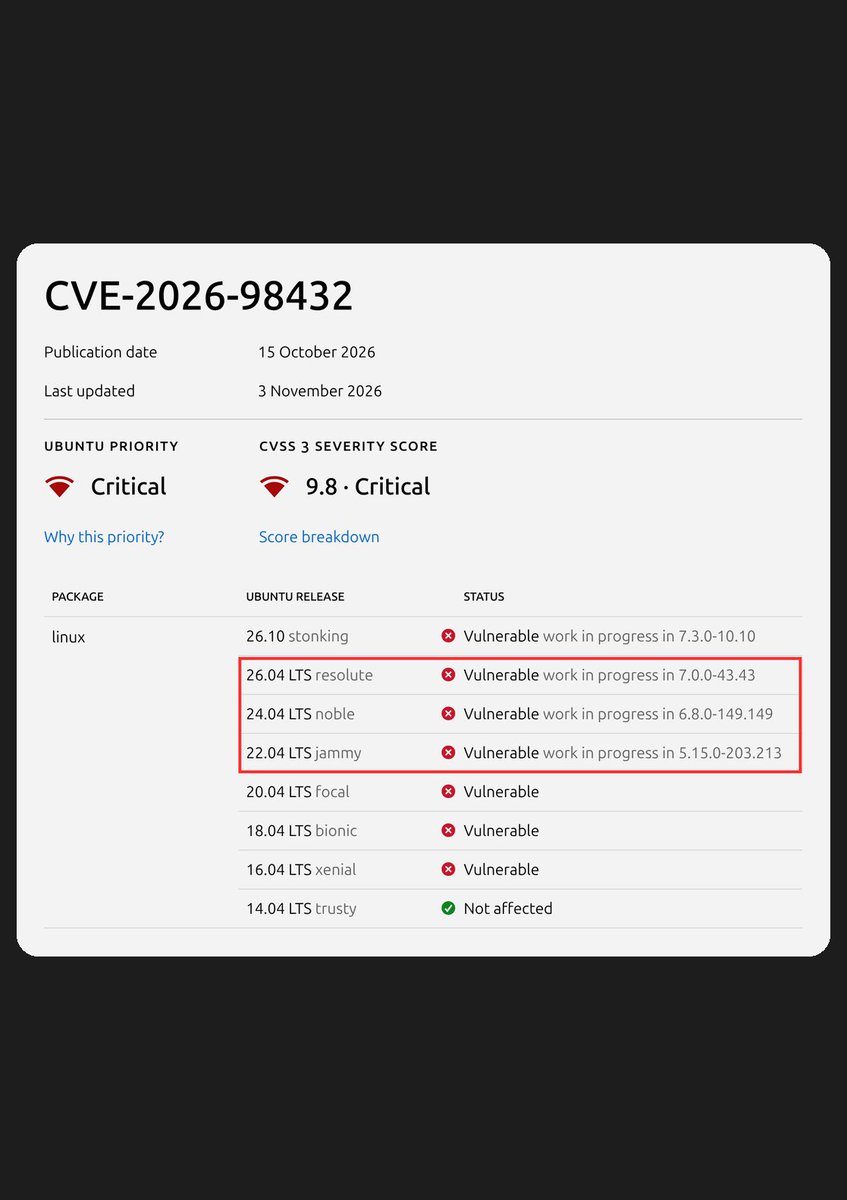
‼️ Attackers are scanning the whole internet for Linux servers exposed to a critical 9.8 kernel flaw, Marcus Hutchins says.
They found 2.1M servers that accept it.
Ubuntu still has no patch.
The bug, CVE-2026-98432, is a race condition in the code that handles incoming IPv4 TCP connections. It can let a remote attacker run commands as root during the handshake.
@ubuntu seems to be struggling with a two line code change to address a security vulnerability (https://t.co/enbtI7ANNT) as bad and potentially worse than the recent PHP exploit.
The two lines of code : https://t.co/2iIfb32XEn
@ubuntu seems to be struggling with a two line code change to address a security vulnerability (https://t.co/enbtI7ANNT) as bad and potentially worse than the recent PHP exploit.
The two lines of code : https://t.co/2iIfb32XEn