🚨 ANNOUNCEMENT FOR TOP CONTRIBUTORS! 🚨
We’ve been working on something huge and the cat 🐈 is finally out of the bag 👀 ... https://t.co/x0TWKNn9PP and Spamhaus have officially partnered with Modat (@modat_magnify) to give FREE Magnify licenses to our top contributors! 🎉🔥
You give your time, brainpower, and expertise to this community 👏. You hunt down the bad guys every single day - we want to make sure you have the best tools 🛠️ to do what you do for the good of the internet every single day!
Consider this our way of saying THANK YOU 🙏 🙏
Top contributors - keep an eye out, we'll be reaching out in the coming weeks to get your access sorted.
More details in comments 👇
Our SYS initiative continues to accept tips regarding cybercrime. If you have information about any threat actor group, you can reach us directly through our TOX anonymously:
D0E5B14B166D8440E3F54CDFC0F38E5080645F728F02AADFB7B978F9D579EE5A6D38A29DD307
P.S. Our graphic designer is away this week, but since posts with images receive better engagement, we did our best. Thank you for your understanding.
#cybercrime #cyberthreatintel #proactivedefense
TR & EN | Dostlar selamlar 🙏🏻 Local LLM inference ve agentic orchestration altyapımı, sanal bir Virtual Coding Cluster / Agentic Developer Team mimarisine evrilttiğim projemi şekillendirmeye başladım. Bu yapıyla yerel inference node’ları, görev yönlendirme katmanı ve rol-bazlı otonom ajanlardan oluşan, modüler ve deneysel bir 7/24 geliştirme ortamı olarak tasarladım.
Mevcut donanım altyapım:
•1× M3 Ultra Mac Studio (512 GB Unified RAM)
•4× M4 Mac Mini (16 GB)
•2× NVIDIA DGX Spark (128 GB)
•2× Raspberry Pi 5 (8 GB)
•1× 24-port switch
Mimari yaklaşımda, LLM inference yükünü belirli düğümlerde konsolide ederken, diğer sistemleri agentic execution / orchestration için konumlandırıyorum. Böylece görev ayrıştırma, kod üretimi, gözden geçirme, test ve rol bazlı iş paylaşımı süreçlerini kapalı devre bir ağ yapısında deneysel olarak çalıştırmayı hedefledim.
İlk fazda odağım, bu sistemi bir Virtual Developer & Security Team yaklaşımıyla test etmek olacak, oldukça heyecanlıyım. 🙏🏻🧡😊 Özellikle çok ajanlı iş akışlarında virtual olarak teknik liderlik, kodlama, QA ve dokümantasyon rollerinin koordinasyonunu ölçümleyerek deneysel bir hiyerarşi oluşturuyorum ve sürecin sonunda daha kararlı ve tekrarlanabilir bir agentic geliştirme hattı oluşturmayı amaçlıyorum. Bir sonraki adımda, mimari çıktıları ve deneysel bulguları teknik notlarla paylaşacağım. 🙏🏻🧡
Hi friends 🙏🏻 I’ve started shaping a project in which I evolved my local LLM inference and agentic orchestration infrastructure into a Virtual Coding Cluster / Agentic Developer Team architecture. With this setup, I designed a modular and experimental 24/7 development environment composed of local inference nodes, a task-routing layer, and role-based autonomous agents.
My current hardware stack:
•1× M3 Ultra Mac Studio (512 GB Unified RAM)
•4× M4 Mac Mini (16 GB)
•2× NVIDIA DGX Spark (128 GB)
•2× Raspberry Pi 5 (8 GB)
•1× 24-port switch
From an architectural perspective, I am consolidating the LLM inference workload on selected nodes while positioning the other systems for agentic execution / orchestration. This allows me to experimentally run task decomposition, code generation, review, testing, and role-based work distribution processes within a closed-loop network design.
In the first phase, my focus will be to test this system under a Virtual Developer & Security Team approach, and I’m very excited about it. 🙏🏻🧡😊 In particular, I am building an experimental hierarchy by measuring the coordination of virtual technical leadership, coding, QA, and documentation roles in multi-agent workflows, with the goal of establishing a more stable and repeatable agentic development pipeline by the end of the process. In the next step, I will share the architectural outputs and experimental findings with technical notes. 🙏🏻🧡
In recent weeks, our research team’ve identified a sophisticated phishing campaign targeting Türkiye. Threat actors targeted computers running Windows operating systems located in Türkiye and using the Turkish language.
Key takeaway: the malware bypassed every public sandbox and AV aside from https://t.co/j39q290bg4, and also evaded EDR/XDR in real-world incidents. We noted impact across many banks, ISPs, and mid-level organizations.
This case again shows why on-premises sandboxes are essential for critical infrastructure and why real dynamic analysis is crucial for SOC teams.
https://t.co/9tyXk8ZVTI
🚨 Search for software, end up getting ransomware!
SEO-driven #Bumblebee malware campaigns observed throughout July led to domain compromise, data theft & #Akira ransomware. Tools included #AdaptixC2 & #Netscan.
https://t.co/vfPxUqnQ9s
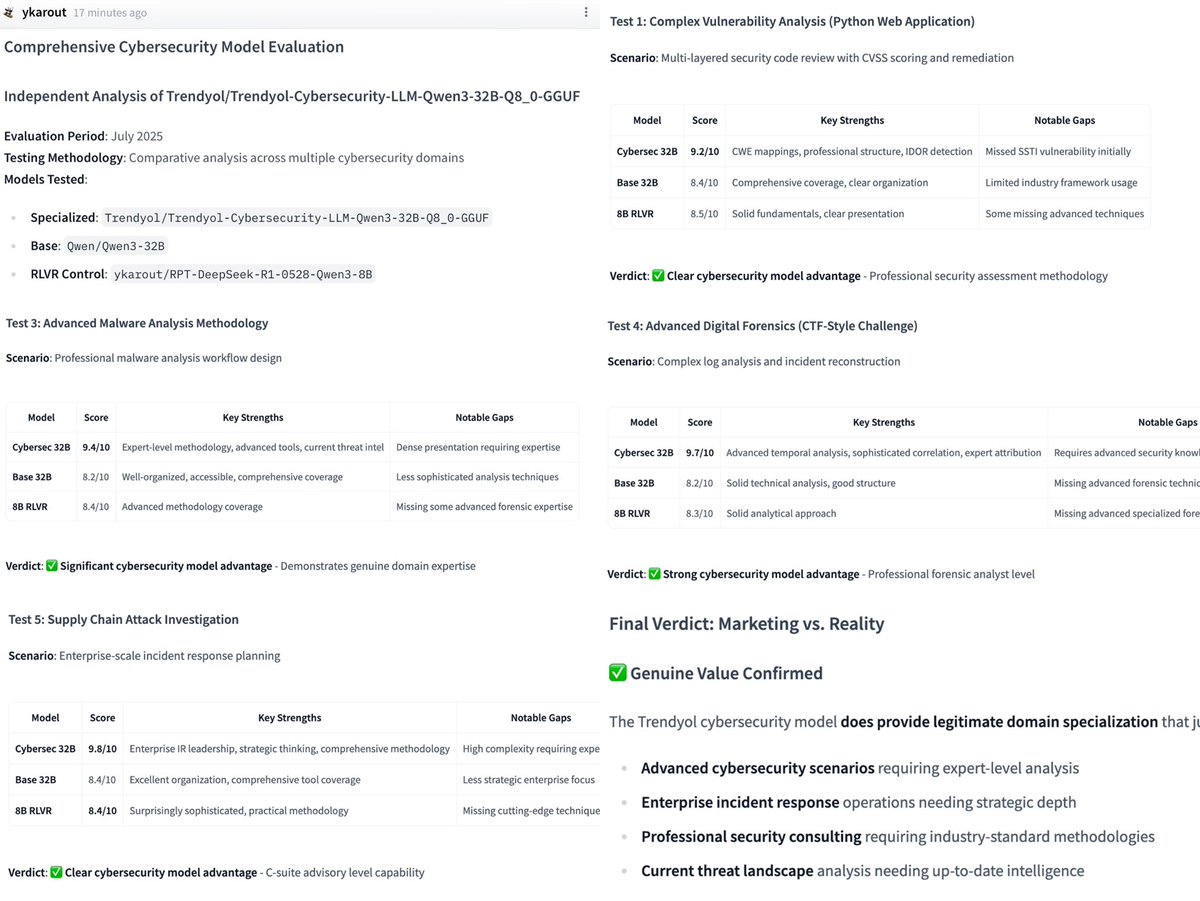
Dostlar Selamlar 🙏🏻🧡 Trendyol Cybersecurity LLM Model’imiz yapılan bağımsız CyberSec benchmark testlerinde harika puanlar aldı. Siber güvenlik alanında şuan rakibi Google sec-gemma ile kıyasıya yarışan en iyi modellerden diyebiliriz. 🙏🏻🥹 İnanılmaz mutluyum 🙏🏻🧡🧿
Huggingface üzerinde bu testi gerçekleştiren “ykarout” nickname’li kullanıcıya çok teşekkür ederiz. 🙏🏻🧡
Testin tam çıktısına aşağıdaki linkten ulaşabilirsiniz: https://t.co/2KEMXfmAEA
🌟New report out today!🌟
Hide Your RDP: Password Spray Leads to RansomHub Deployment
Analysis and reporting completed by @tas_kmanager, @iiamaleks and UC2
🔊Audio: Available on Spotify, Apple, YouTube and more!
https://t.co/jL4oy28kS0
🚨 New #ClickFix scam targets US users with fake MS Defender and CloudFlare pages.
⚠️ The scam page is hosted on a domain registered back in 2006, pretending to be the Indo-American Chamber of Commerce.
🎯 The #phishing page loads only for US-based victims, as observed during analysis with a residential IP in #ANYRUN Sandbox.
👨💻 Analysis session: https://t.co/4Wg8mM2De5
📍 URL: iaccindia[.]com
The page hijacks the full-screen mode and displays a fake “Windows Defender Security Center” popup.
🎭 It mimics the Windows UI, locks the screen, and displays urgent messages to panic the user.
Victims are prompted to call a fake tech support number (+1-…), setting the stage for further exploitation.
🎣 The phishing page may also display a fake CloudFlare message tricking users to execute a #malicious Run command.
Take a look: https://t.co/OAWXHsJ1tV
#IOCs:
supermedicalhospital[.]com
adflowtube[.]com
knowhouze[.]com
ecomicrolab[.]com
javascripterhub[.]com
virtual[.]urban-orthodontics[.]com
Streamline threat analysis for your SOC with #ANYRUN 🚀
#ExploreWithANYRUN
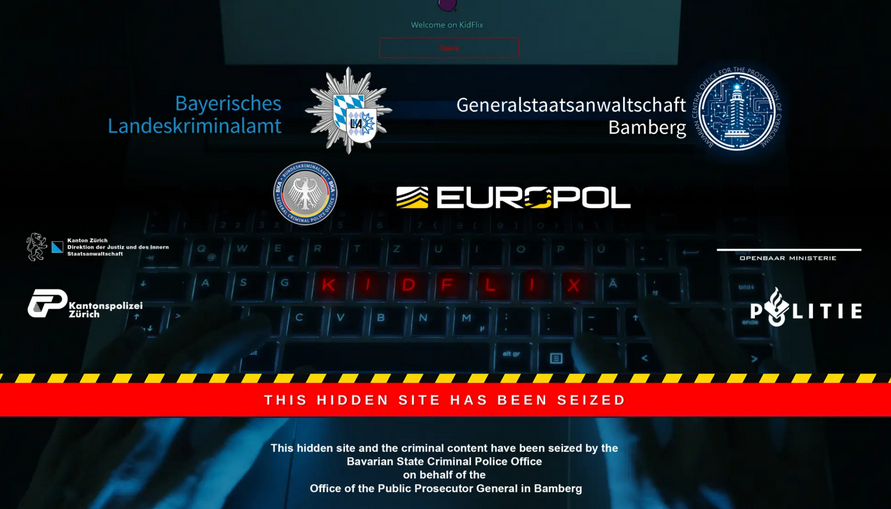
Today EUROPOL announced the takedown of a large and prolific CSAM (Child Sexual Abuse Material) website known online as "Kidflix" — a reference to Netflix.
Over 35 countries were involved in the operation which was lead by the State Criminal Police of Bavaria (Bayerisches Landeskriminalamt) and the Bavarian Central Office for the Prosecution of Cybercrime (ZCB).
Kidflix was infamous due to it's "unique" features for CSAM websites. It allowed users to filter by video quality, watch child abuse livestreams, and preview videos prior to purchase. Additionally, individuals who were active on the website, shared content, produced unique content, etc. could earn "Kidflix tokens" which allowed them to get other CSAM material for free. Furthermore, the site had 3.5 unique CSAM videos uploaded every hour, with a total of 6,288 hours (262 days) of CSAM videos present on the website.
Law enforcement learned over 1,800,000 people from all across the globe visited Kidflix. Kidflix contained over 72,000 videos of CSAM.
As a result of the takedown over 1,400 suspects have been identified and (thus far) 79 individuals have been apprehended and 39 children has been rescued from child predators.
This operation, dubbed "Operation Stream", is the largest pedophile network takedown European history. EUROPOL has stated they will continue to work with other countries law enforcement agencies to hold each person accountable for the crimes committed on Kidflix.
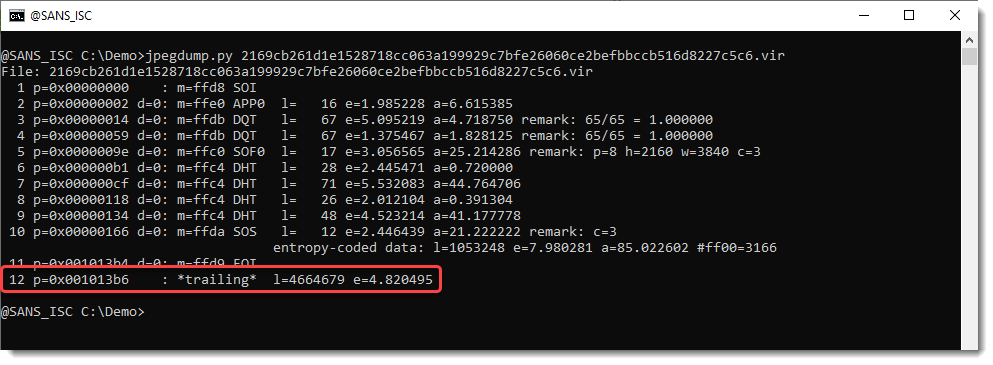
My webinar "Decrypting RDP Traffic in Wireshark" went well this morning, we had over 150 attendees out of 330 people registered. As promised, here are the slides for the presentation: https://t.co/3lq5hvFH6f