Pentesters: already living in Burp Suite?
DoubleAgent connects Agent A (Burp extension) → YOU → Agent B (AI teammate).
Review findings. Question assumptions. Guide the next step.
Open-source beta 👇
https://t.co/8FWNQ9DUe4
#BurpSuite#Pentesting#AI#AIAgents#AgenticAI
@elliotarledge@TheZachMueller granted, but it's about the same results for blackbox web pentesting too. I think DS 1017 is slightly ahead rn, but just saying it's pretty close if you find a good checkpoint.
@HackingLZ it'll come in time. Current models are perfectly capable, but right now there's no need to find novel attacks on an internal as it's just too easy. Maybe try asking the agent to take the hardest path possible to DA :)
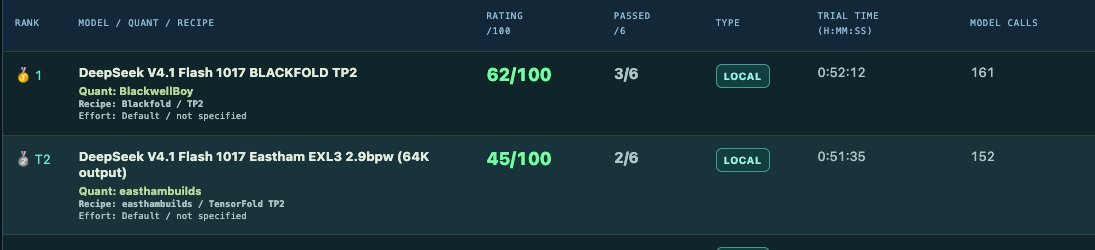
@NullBurn@ivanfioravanti yes, that one came in with the same score on medium, but for some weird reason it won't complete on easy. I'll try again with the latest recipe today
Which local model and serving recipe can actually hack? We put the quants through black-box web and network challenges, compare verified results, and see how they stack up against cloud-hosted models.
https://t.co/JFieSdkpSt
Before local AI is banned, learn how to host and tune your own models.
Specific learning curves to understand for me were:
- Offloading portions of newer models to SSD rather than RAM
- Prompt caching configs
- Preload tuning
- the right choice of model for the task
- pre optimized models for your hardware and harness
- finding the fastest inference server at the web/api level
Claude can no longer “Reverse Engineer Anything.”
Anthropic just quietly killed REA.
But Interesting timing.
After a few viral cases of people using Claude to reverse-engineer Samsung TV firmware and identify data-collection services, Anthropic appears to have restricted those reverse-engineering abilities.
@ivanfioravanti I tried it today and it pretty much aced a network pentest - which invokes a LOT of tool calling. Its the first DS I’ve tried tho. Web testing results to follow.