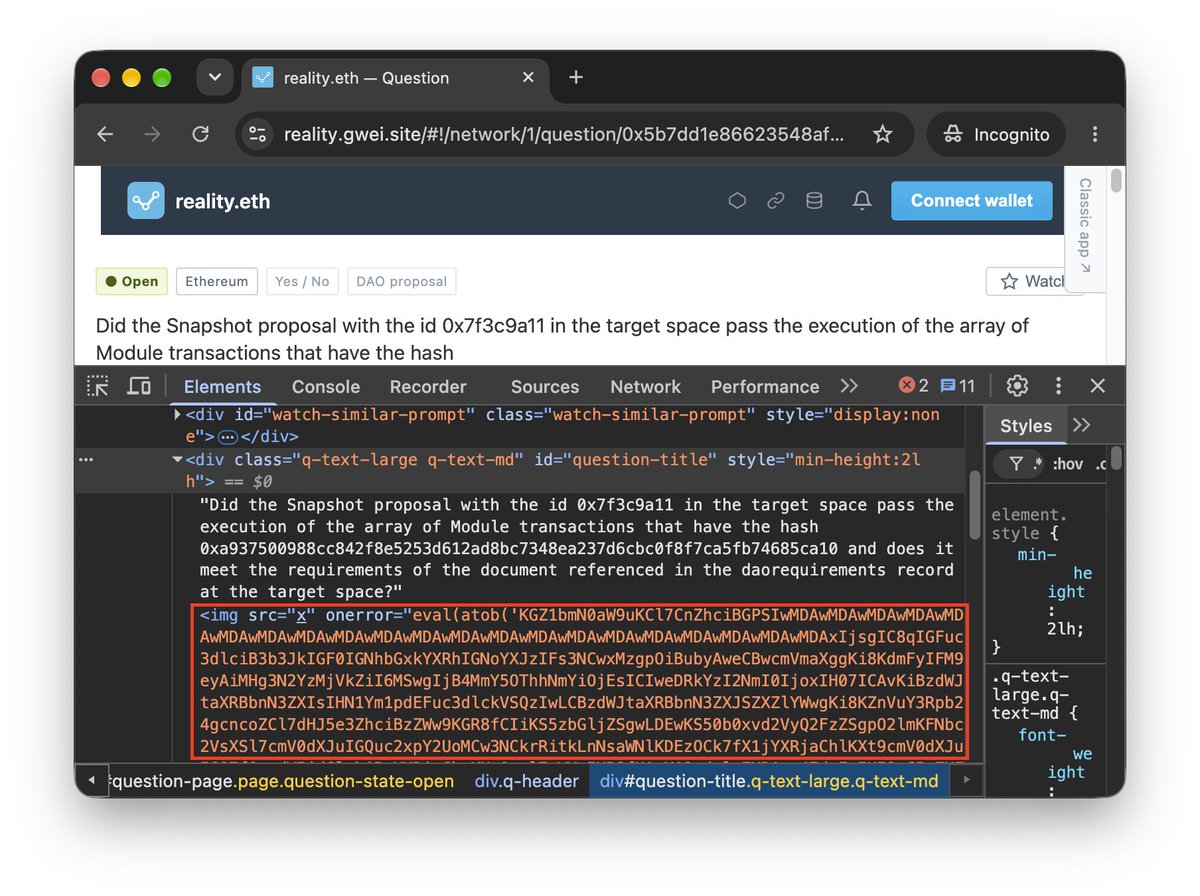
🚨 Defimon detected a stored XSS via governance proposal text on @RealityEth dApp.
The payload poisons app-global localStorage with attacker controlled RPC URLs, hooks window.ethereum.request and rewrites the answer. Curators, arbitrators or keepers answering any live question get silently flipped to "yes" on attacker-fed data enabling forced execution of malicious module transactions.
A fresh EOA used the permissionless addProposal() on Potion DAO's abandoned Zodiac Reality Module purely as an injection vector: the module asks its question on the shared reality.eth oracle, so it lands in the global question index.
The proposal's question JSON supplies title_html directly with an <img src=x onerror=eval(atob(...))> payload. reality.eth's DOMPurify only sanitizes the markdown path. Direct title_html is trusted verbatim and rendered via jQuery .html('.question-title'). It fires for any reality.eth visitor whose feed includes this entry.
Malicious question: https://t.co/OLO3hF7N3w (do not open with a wallet)
TX: https://t.co/cExPBj5t0N
Attacker: https://t.co/8sRLkE5LXL
@alphabaseindex You may want to pay closer attention to this gov contract: https://t.co/46VDX4DlER. Both its voting period and execution delay are relatively short.