"The world’s biggest Apple security conference [#OBTS] kicks off this week in Hawaii" 🍎🛡️👾🐛
https://t.co/snTXKcRKiZ (by @arinwaichulis)
See you by the Sea! 🏖️
Been a while since I've donated blood but I did it yesterday. Was surprised at how easy it went, felt fine afterward. Consider this your periodic reminder that you can save a life at very little inconvenience to yourself!
Noriben for malware analysis v2.1.0 release:
https://t.co/kWfSu7fAGU
* ASCII graphical process tree
* Monitors DLL loading
* JSON output
... and more
I hinted to this before but never fully announced its release
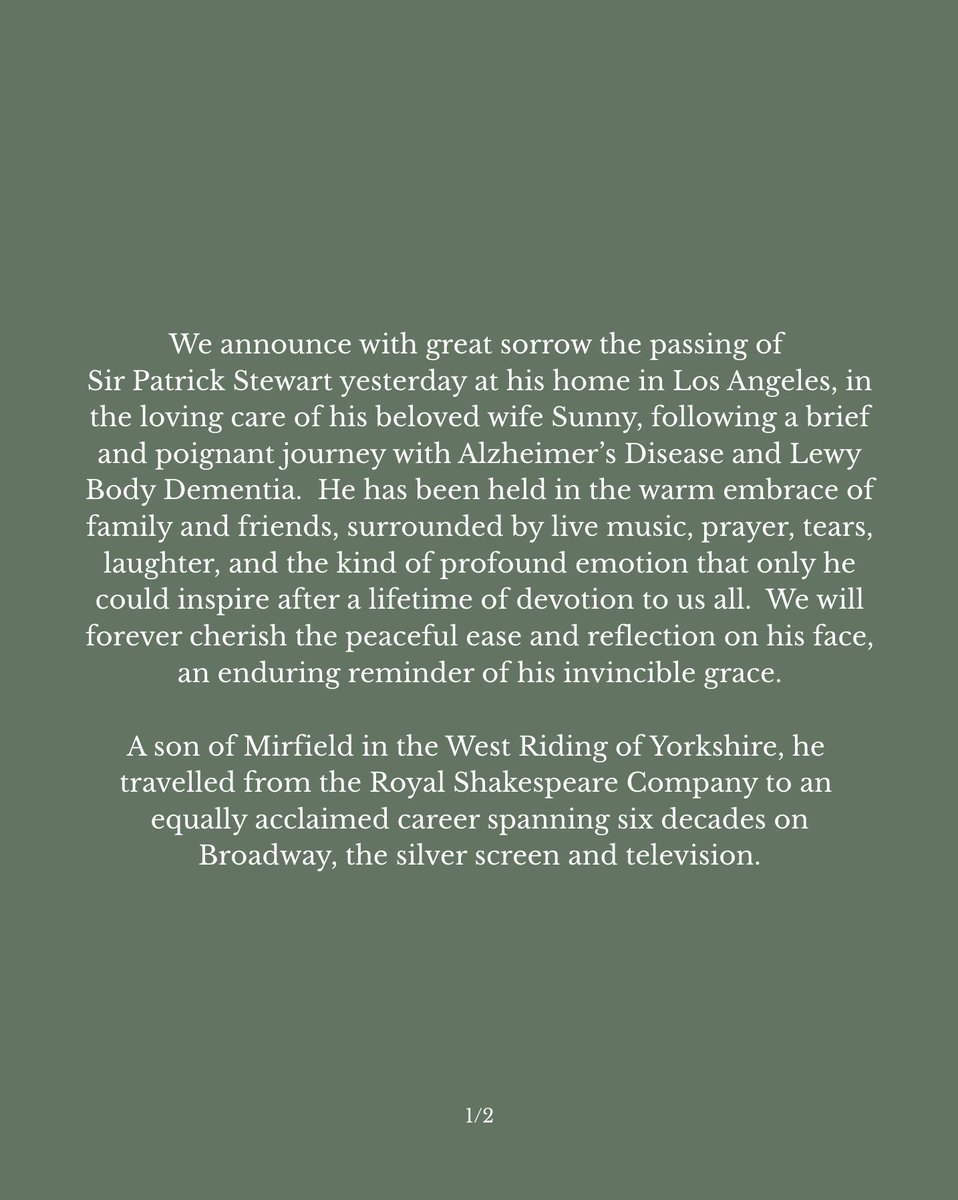
In lieu of flowers, memorial contributions may be made to:
Johns Hopkins Alzheimer’s Disease Research Center Fund
https://t.co/luC5CdcWDy
Alzheimer’s Foundation of America Caregiver Resources
https://t.co/zvNptfyuNd
Photo Credit: Tommy Garcia
#OBTS v9 schedule is LIVE! 🔥
https://t.co/3pvSvOoVcO
If you're into Apple security (yes, including securing those pesky AI agents 🤖), you seriously don't want to miss this one!
Hope to see you by the sea ☀️🌊
And once a Mac is exploited, you can interact with any of the users "connected" devices also running Muse.
...meaning you remotely task their mobile (iOS) Muse client ...invisibly 📲🔓👀
What can you do? Welll, some very neat iOS stuff!
As I was writing Day 4 content about a sandbox escape vulnerability, I added a whole section about GateKeeper internals as well.
Interested in finding that 100k$ GK bypass vulnerability? Join our training and understand the basics so you know how to get started!
Only in Budapest this year.
Lorenzo has always been solid, professional, and loves telling stories from an accurate perspective with the correct details.
Highly recommend for any fellow hackers, tech, and related fields.
Wishing you the best always
I've just (re)written TaskExplorer
Think Process Monitor but for macOS, open source, & much more powerful 💪🏽
Highlights:
• CLI + JSON export
• On-device AI assistant
• Code signing + VirusTotal context
• Live process/file/dylib/network activity
https://t.co/1rfeBWoEVE
fashion 1.2.0 is out 🎉
macOS 27 adds a third slice to every system binary, arm64e.x1. fashion now names slices exactly as codesign does, so nothing hides behind a plain arm64.
Hash, match and triage Mach-O: SHA-2, ssdeep, TLSH, CDHash, symhash.
https://t.co/bIt5lVOaRh
Was stoked to talk nerdy with @arinwaichulis & Kseniia (@osint_barbie) about the ever-changing macOS threat landscape, Apple’s bug bounty changes, #OBTS v9, and more 🍎🤓 Have a listen!
This is an an excellent lineup of talks, and I'm honored to present again, along with @gergely_kalman . We will hack macOS like it's the 80s!
This will be my 7th OBTS talk, can't believe time flies so fast.
My favorite conference, small, awesome speakers, people, great community, great chats for 3 days, can't wait to be back ❤️
Just announced: talks for #OBTS v9 🥳
Stoked on an epic lineup of cutting-edge 🍎- security research, covering exploitation, malware, reversing, security tools, AI, & more!
Check out the full lineup:
https://t.co/aGwpUhN2xZ
Which one(s) are you most looking forward to!? 🤔
The latest macOS ClickFix variant invisibly mounts DMG images in the background to execute a macOS infostealer and hijack cryptocurrency wallet info. Details at https://t.co/8Bg5ojzg26
@patrickwardle@jbradley89 3️⃣ "Practical iOS Reverse Engineering"
https://t.co/gvdoVH4ZEV
Join @naehrdine for this hands-on training covering iOS app reversing, Frida, Ghidra/IDA, XPC, kernel & firmware internals, & the latest iOS security mitigations.
From beginner fundamentals to advanced iOS internals
The 2025 @volatility#PluginContest review is complete! We received 8 submissions from 7 different countries that included 20 plugins!
We will be highlighting each #Contender & the winners will be announced on Friday!
#DFIR#memoryforensics
🧵 1/ What a funny story how @g0njxa and I decided to start trading and download TradingView Premium for FREE! (freaking AI is gonna replace us, so...) xD
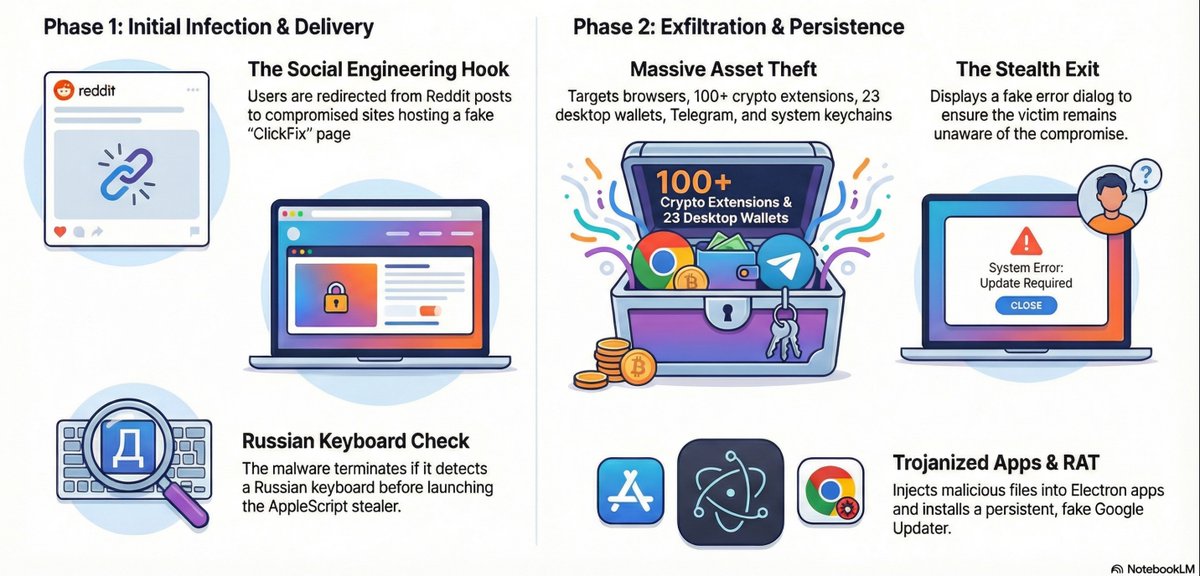
Check this macOS stealer campaign that is using @Reddit karma-farming, allegedly compromised Indian tech company as a redirect, and a ClickFix trick to deliver the SHub Stealer that steals sensitive data, trojans your crypto wallets, and tries to persist disguised as Google Updater.
But don't worry - if you have a Russian keyboard, it won't touch you :3