Extraordinary: A selection of multi-planet systems found in the Milky Way galaxy thanks to the Kepler Space Telescope!
(Credit: Ethan Kruse/NASA Goddard)
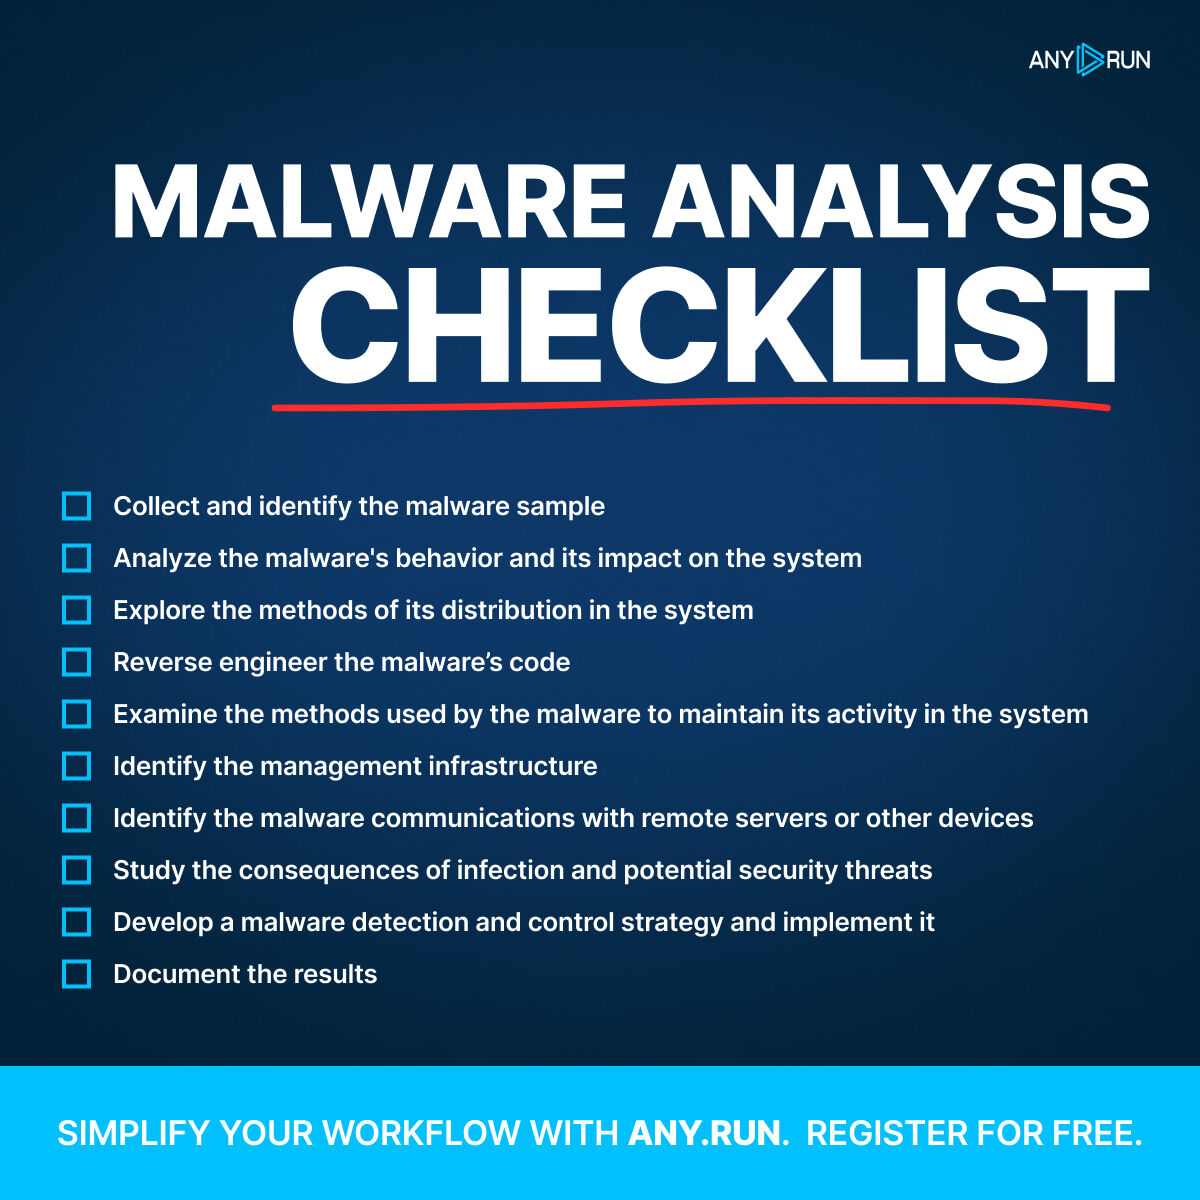
📝 This checklist can help you stay organized and ensure that you don't miss anything during your #malware analysis
Simplify your workflow, analyze malicious files and links with #ANYRUN 👉 https://t.co/37jWtOhL0e
🟧 #HackTuesday 🟧
Hack Tuesday: Week 12 - 18 Jun 2024
⚠️ 100 ransomware victims all over the world by 27 hacking groups ⚠️
Check out our carousel for a quick look!
For the complete list, follow the link:
https://t.co/yUhpTOzzsM
#Ransomware #DataBreach #CyberAttack #H🟧 #HackTuesday 🟧
Hack Tuesday: Week 12 - 18 Jun 2024
⚠️ 100 ransomware victims all over the world by 27 hacking groups ⚠️
Check out our carousel for a quick look!
For the complete list, follow the link:
https://t.co/yUhpTOzzsM
#Ransomware #DataBreach #CyberAttack #H🟧 #HackTuesday 🟧
Hack Tuesday: Week 12 - 18 Jun 2024
⚠️ 100 ransomware victims all over the world by 27 hacking groups ⚠️
Check out our carousel for a quick look!
For the complete list, follow the link:
https://t.co/yUhpTOzzsM
#Ransomware#DataBreach#CyberAttack#HT
As a detection engineer writing detections for a product. You'll face the reality that you need to write the same detection using multiple sources
- Security Log
- Sysmon
- PowerShell Scriptblock (if its powershell related)
- Kernel / EDR source
- ETW counterpart Kernel-Process / Kernel-File...
🙃
No one talks about this shit. Because every customer could have different things enabled......
My lifespan is shortened with every CVE 😭
Someone has built a huge regex to cover many obfuscated versions of the log4shell payloads
Really nice, I'll test it and update my gist
Repo
https://t.co/PWEhw7uir5
Test
https://t.co/FSMzCBsBTT
7\ If you want to visualize your EVTX and do all these fancy stuff like graphs, filters and play around with any charts, I highly recommend my friend's project made from ELK and different parsers, all for DFIR folks. Shoutout to my friend @Maboalenen
https://t.co/mS4fbunRZb
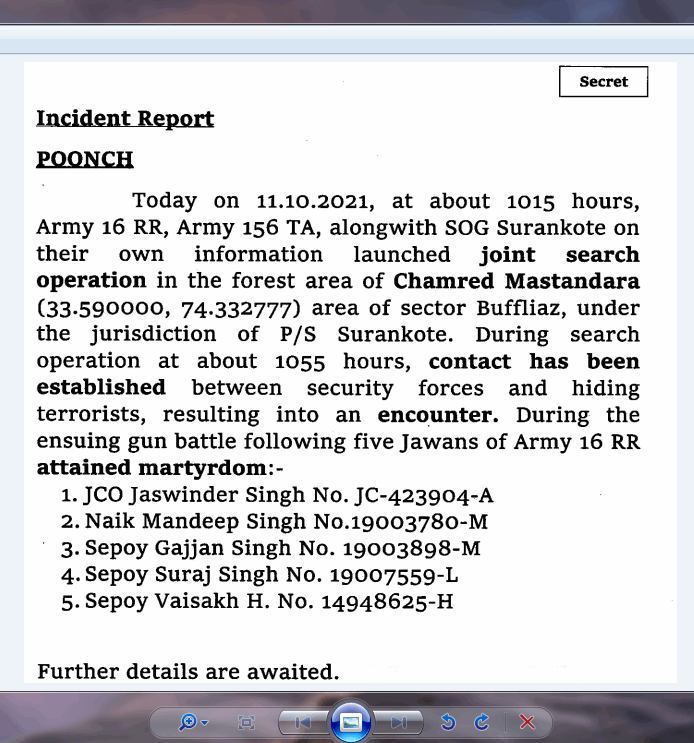
New sample probably from #Sidecopy#APT:
After execution, the sample will download and display images related to Incident Report to confuse the victim and execute the malware for remote control.
d78e8943a1a2932d094957ef47956324
4c4b00e6a03b8e71f7da147450ea424a
C2: 62.171.187.53