Ever measured how late your logs actually arrive?
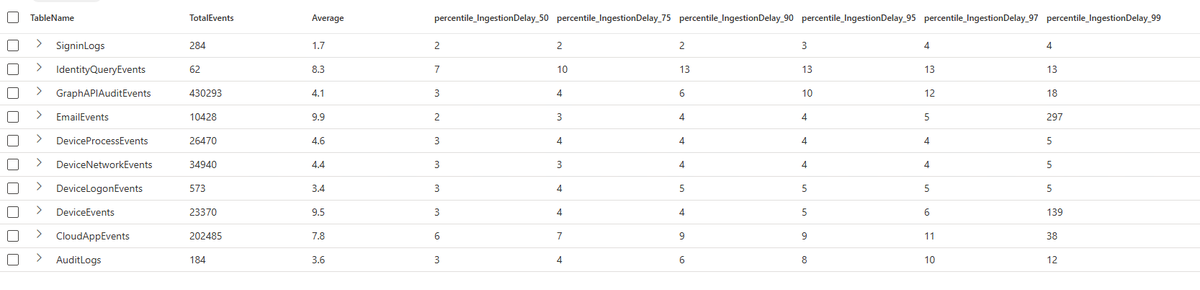
ingestion_time() − TimeGenerated = your real ingestion delay, per table.
Use percentiles, not averages - buffered endpoints skew the mean hard.
@BertJanCyber tenant:
• 50% of DeviceEvents landed within 3 min
• 97% within 6 min
Your detection’s search window should know this number.
More in his blog:
https://t.co/jT5SqHW9S9
Ever seen ssh.exe on a workstation and ignored it?
That -R flag opens a SOCKS pivot. Akira's operators used it to proxy a scanner before dropping ransomware.
Your EDR sees ssh.exe. Nothing inside the tunnel.
The network telemetry still leaks. Here's how to read it 👇
Catching up on Linux malware and I saw TrendMicro talking about Quasar Linux Remote Access Trojan. Sandfly finds this very noisy piece of malware easily. Let's talk a bit about what it's doing.
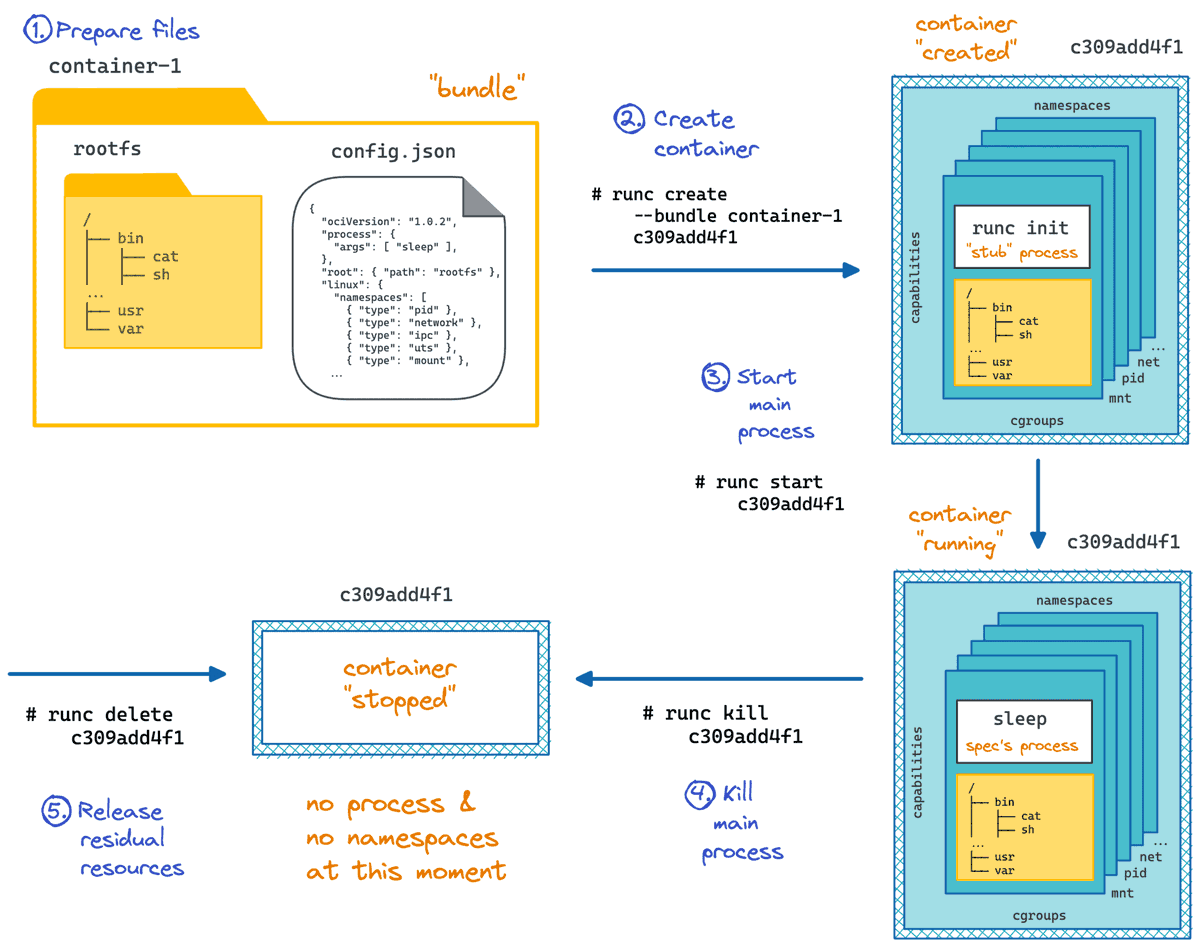
Three years ago, I started building an interactive learning platform to help people master Linux, networking, Docker, and Kubernetes in a visual and hands-on way.
Today, iximiuz Labs has:
- 60+ remote Linux playgrounds
- Dozens of interactive tutorials
- 100+ practical challenges
- A growing cohort of great authors
...and most importantly, 34.2 registered students with over 2,000 daily active users 🤯
Developing and operating a platform of such scale has become my full-time job, and honestly, the workload is outgrowing my capacity as a single-person SaaS founder. A proper team is becoming increasingly necessary.
If you're one of the students considering switching to the premium tier, now is the best time. On the premium tier, you will get:
- Full access to all current and future learning materials published by the iximiuz Labs team
- Twice bigger playground VMs with no daily usage time limit
- The ability to store the playground state and restore it later on
...and a whole bunch of smaller perks.
Why now? With the Black Friday deal, both the subscription and the lifetime plans are no longer a steal but a robbery. But there might be an even bigger reason - even undiscounted, the all-inclusive lifetime premium access is not a sustainable way to run an edu business, so all sales of this plan are going to stop by the end of the year. So, now _is_ the best time:
https://t.co/5HI4zLAFfR
P.S. Of course, all revenue from the sales is reinvested in the platform's continued development 💪
🚨 #DFIRtips 🚨
Today, during an investigation, I found a registry key that proved to be extremely useful in identifying the execution of a malicious executable: HeapLeakDetection!
You can find it in the Software hive, specifically at HKLM\Software\Microsoft\RADAR\HeapLeakDetection\DiagnosedApplications.
This registry key is interesting because its subkeys refer to all the executables that have been detected by RADAR technology for real-time memory leak detection.
Each subkey has its own LastDetectionTime which tells us the last time a memory leak occurred and which executable was affected.
Even though it is not particularly well-known, this artifact could sometimes turn your investigation around, especially when the threat actor tries to erase their tracks by deleting the most common artifacts (Prefetch files, evtx logs, etc.)
[screenshots from my test machine]
🚨 Mandiant observed #LummaC2 stealers leveraging a new obfuscation technique to thwart analysis tools and stifle reverse engineering efforts.
Read about this tactic, and how we developed an automated method for removing this protection layer → https://t.co/lGWQQySlZI
Hey Friends,
I am currently running a promo on my course of "Offensive Development and Tradecraft" which will give you 20% off and bring the price down from $529.99 to $423.99.
Master Offensive Development with Over 12 Hours of In-Depth Video based content!
In this comprehensive course, you'll acquire essential skills for Offensive Development, including techniques for bypassing Yara Rules, Direct/Indirect Syscalls, Api Hooking, Module Stomping and Crafting position-independent code (PIC) in C. Development tech includes Mingw, Cmake and Python.
Course Highlights:
Foundations in C Programming and Assembly Language: Build a strong base to develop and understand complex code.
Deep Dive into Windows Internals: Explore the intricacies of the Windows operating system to enhance your development strategies.
Hands-On with Industry-Standard Tools: Learn to use x64Dbg and IDA Pro for advanced reverse engineering, giving you the tools to investigate and understand Windows Internals effectively.
cc: @DfirDiva
1/2
From initial access to Domain Admin... with a detour through Entra. Another real example from a real environment.
We will demonstrate the discovery, execution, and remediation of this specific attack path in this webinar on August 22: https://t.co/337bxXbPjN
Did you know about the SysNative alias in Windows?
"SysNative" is a special alias that allows 32-bit applications to access the 64-bit system directory (System32) on a 64-bit operating system.
Windows 64-bit operating systems include a compatibility layer called "Windows on Windows 64-bit" (Wow64), which allows 32-bit applications to run. This layer redirects access to certain system directories to ensure compatibility: When a 32-bit application requests C:\Windows\System32, it is redirected to C:\Windows\SysWOW64 (which contains 32-bit binaries).
A 32-bit application or script might need to access a 64-bit version of cmd.exe or other system utilities located in System32. It can use C:\Windows\SysNative\cmd.exe to ensure it gets the 64-bit version. SysNative is not a physical directory but a virtual alias handled by the Wow64 subsystem.
This alias is only available to 32-bit applications. If you try to access C:\Windows\SysNative from a 64-bit application, it will not be found.
@SwiftOnSecurity has a funny story about SysNative here:
https://t.co/MdDApVKsAA
Or here, a good one from @MalwareJake:
https://t.co/TojFvS4yMB
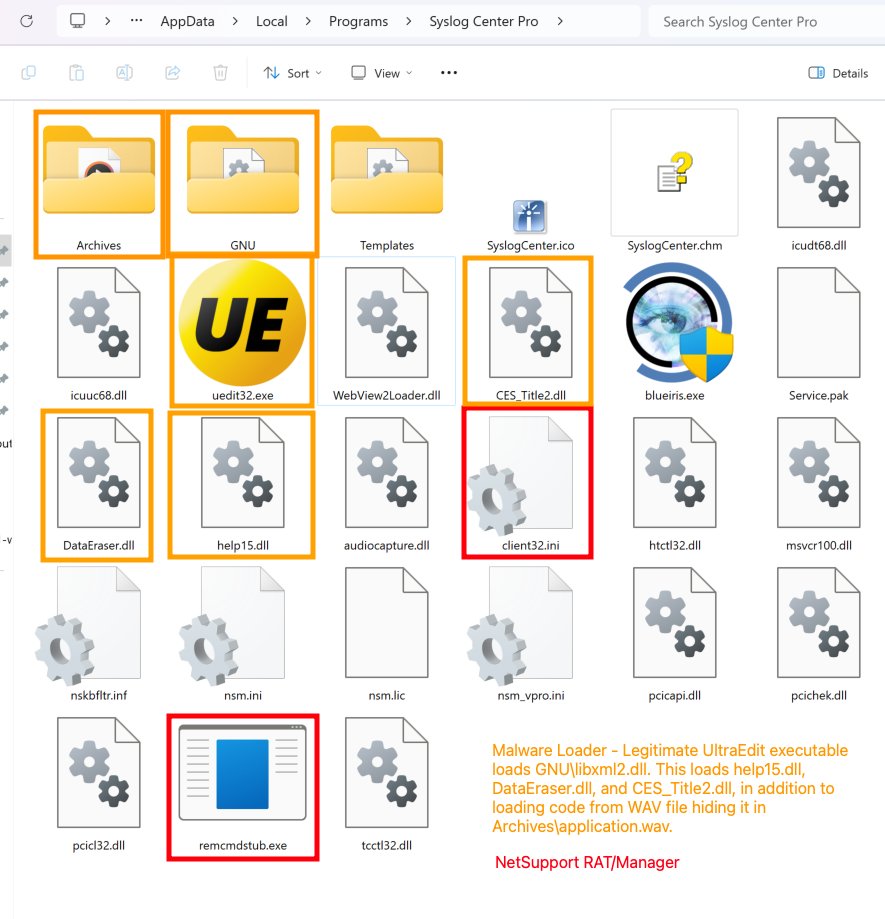
An interesting malware loader here which is almost fully undetected on VT.
https://t.co/1KjuETHjyh
Masquerading as Blue Iris installer.
Downloaded from: christmasxdecor[.]com
Deploys binaries to %LocalAppData%\Programs\Syslog Center Pro\
End result is NetSupport Manager\RAT
NEW COURSE LAUNCH!
"Windows API Hooking"
- Theory
- Inline Hooking
- IAT Hooking
- Hiding processes from usermode process
- DLL Unhooking
- Fixing base relocations
and much more
https://t.co/hfATXN0ZTu
#infosec#malware#redteam#cybersecurity
I am giving away 1 seat for the "Hands-On Kusto Query Language (KQL) for Security Analysts" course.
✅ Lots of hands-on examples in the lessons
✅ A total of 23 exercises
✅ 2 Investigation scenarios
Please Reply, Like AND Repost to participate. The winners will be announced on Friday 6th Feb 2024.
#KQL #SecurityAnalysis #Training #ThreatHunting #IncidentResponse #MicrosoftSentinel #MicrosoftDefender #M365Defender #DFIR #DataAnalysis
🚀 Exciting #Giveaway & Offer! 🎁 Save 20% on the revamped "Hands-On KQL for Security Analysts" course - now with Lifetime Access!
🎟️ Use code "ANALYST23" at checkout before 31.12.2023.
🌟 RT & follow for a chance to win a free seat! Enhance your investigation and #IncidentResponse skills.
🔗 https://t.co/qoSTNy22HM
Stay tuned for more updates!
#KQL