I was human participant no 3 in this research paper.
Stanford paid me (and another 9 humans) to hack their network for 10 hours 😎I found 3 critical vulns, 2 high, 1 med and 1 low, 7 in total.
Their AI agent did pretty well, 11 total vulns, 9 valid.
What is crazy to me is the amount of vulnerabilities they have in their internal network see pages 16-19
We are very happy to announce the nominees for the 2025 Pwnie Awards!
As a reminder, we will be presenting the winners at DEF CON this year. Saturday the 9th, 10:00AM Main Stage.
Hope to see you there!
https://t.co/hWUu2PcM8B
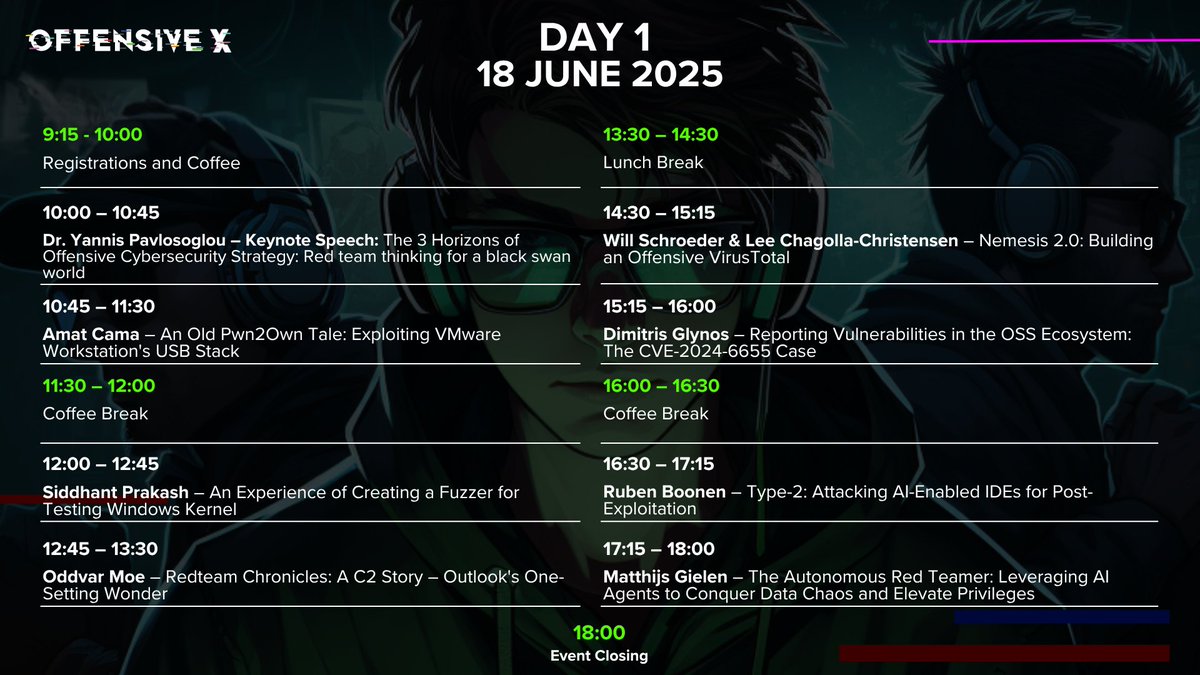
The OffensiveX 2025 Agenda Is Live.
On June 18–19, we’re bringing the sharpest minds in offensive security to Athens to drop real research, real tools, and real tactics.
You’ve seen who’s speaking. Now it’s time to see what they’re dropping.
🔗 Check the full agenda: https://t.co/laFBa0m9Ng
#OffensiveX2025 #OffensiveX #HackingConference #CyberSecurity #RedTeam #ExploitDev #OffensiveSecurity #Infosec
🚨 The wait is over—CFP for #OffensiveX2025 is NOW OPEN.
Got research that challenges assumptions, breaks new ground, or exposes critical security flaws? This is your chance to take the stage at Europe’s most technical offensive security conference.
No fluff. No marketing. Just raw, cutting-edge security research from the industry's top experts.
Submissions are now live and will close on February 28th. If you know someone who should be on that stage, share this with your network.
https://t.co/s5CX1ve37T
#Cybersecurity #OffensiveX2025 #CallForPapers #HackingConference #RedTeam #OffensiveSecurity
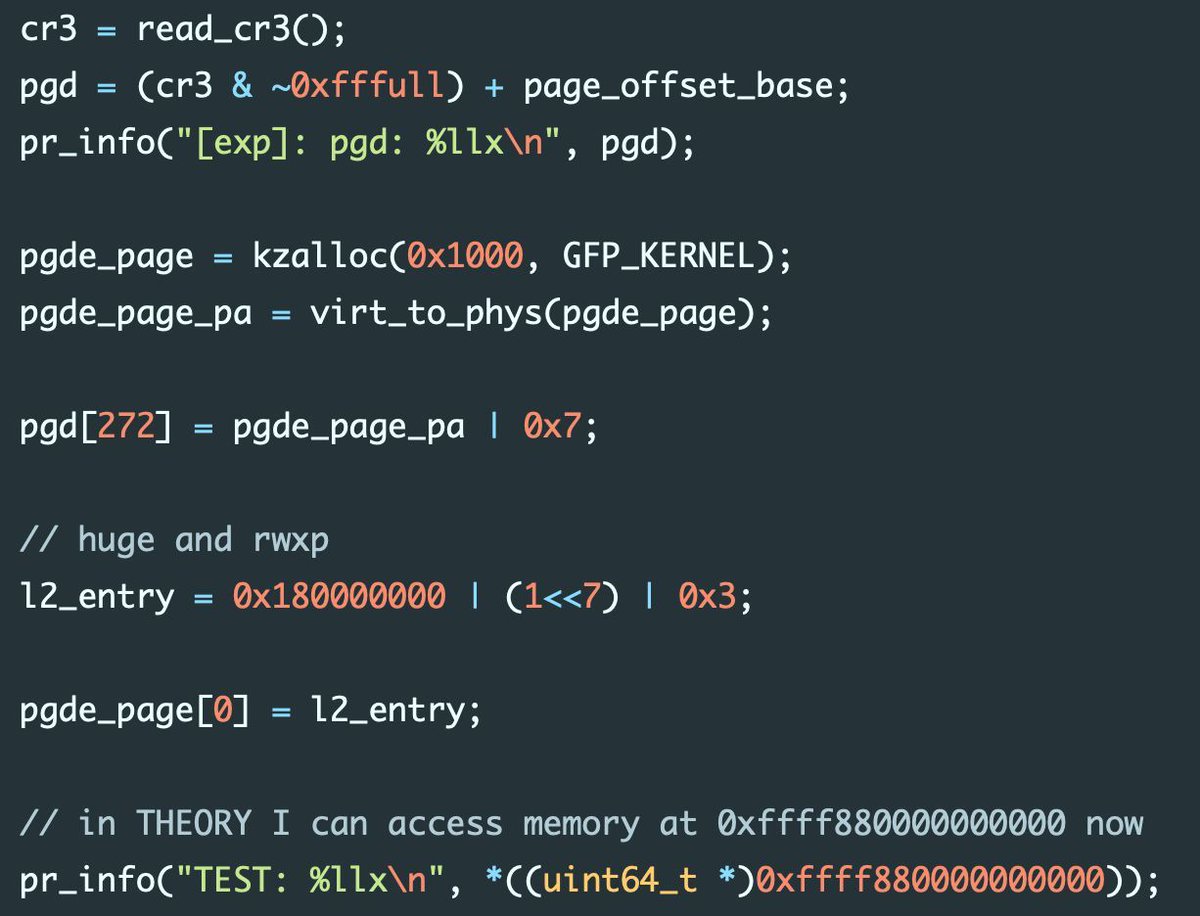
I have posted the slides for the talk @chompie1337 and I gave this past weekend at @h2hconference -> The Kernel Hacker’s Guide to the Galaxy: Automating Exploit Engineering Workflows #H2HC
https://t.co/Cl8b58KkAv
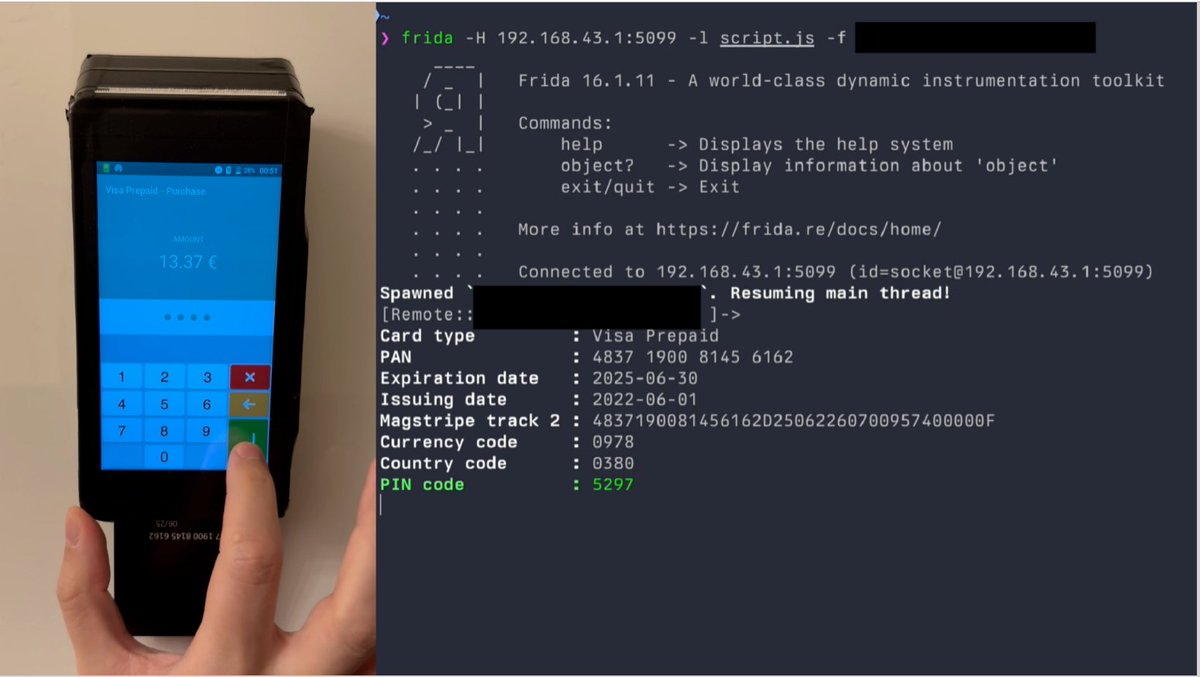
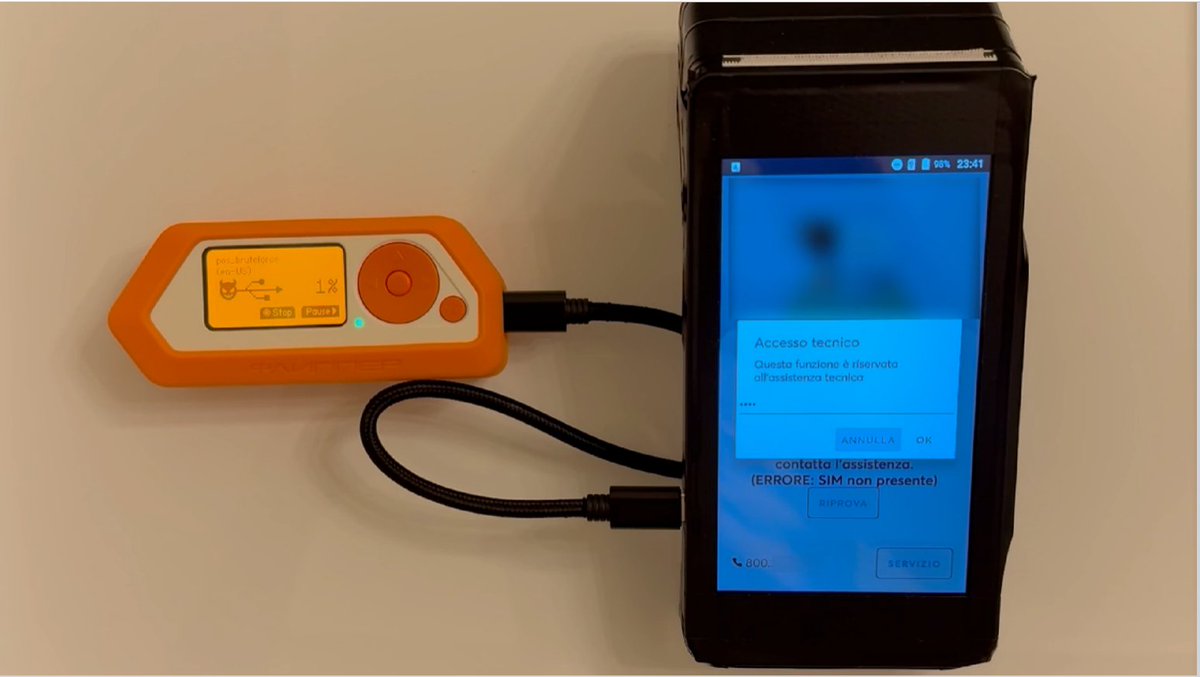
Rooting an Android POS "Smart Terminal" to steal credit card information:✅
Paper "Exploring and Exploiting an Android 'Smart POS' Payment Terminal", by Jacopo Jannone.Paying with a POS will never feel the same for me.
PDF: https://t.co/mZqbgoZZyh
Video: https://t.co/V98uJ4MH0m
The first ever end-to-end cross-process Spectre exploit? I worked on this during an internship with @grsecurity! An in-depth write-up here:
https://t.co/mze3LQkpJR
I just released my C2 I was working on, on my free time. Feel free to play around make your own forks if you like it. It needs a lot of work but it is a fully rust one with small implant and working sleep obfuscation.
https://t.co/kSu1KW6IYN
🔥💀 Here is the "Real" writeup and exploit for the
pre-auth deserialization RCE I reported to Ivanti
CVE-2024-29847
Apparently, folks at horizon3 tried to write about my bug before me but they did it wrong
https://t.co/Df8lIDYNRH
The exploding Hezbollah pagers situation is an incredibly impressive supply chain attack by Israel (most likely). I am sure more details will come, but there are already some educated guesses to be made that narrow it down.
🧵1/n
If you’re interested in getting started in cryptography, check out the crypto 101 course by Dr. Alfred Menezes from UWaterloo.
https://t.co/cevF3j5OTb
He’s planning on publishing the lectures from his Applied Cryptography course, which was my introduction to the field.
"Most concerning is the illusion that LLMs are retrieving information rather than constructing word associations. LLM responses are statistically likely rather than factually accurate. Sometimes these things correspond, but often they do not." E. Salvaggio https://t.co/61IXZ3cipL
🚨We are very pleased to announce the nominees for the 2024 Pwnie Awards! Be sure to tag your friends and catch us at Def Con! 🚨
🥳🏇🥳🏇🥳🏇🥳🏇🥳🏇🥳🏇🥳🏇🥳🏇
https://t.co/TxplA2l6X6